
Threat actors are exploiting a critical command execution flaw, now tracked as CVE-2026-110447, in the Collabora Online – Built-in CODE Server app (richdocumentscode) for Nextcloud.
Multiple administrator reports indicate that the attacks began in mid-September, about a month before the official event Security bulletinThe GitHub AdviceAnd CVE publication.
CVE-2026-110447 affects Richdocumentscode versions before 26.4.303 and is located in the Nextcloud app’s mechanism for starting the bundled Collabora server.
The error only affects the optionally integrated CODE server app. Standalone Collabora Online servers, Docker and RPM/DEB installations as well as Nextcloud All-in-One deployments remain unaffected, according to Collabora.
The attacks involve sending a malicious request to the app proxy.php Endpoint that triggers operating system command injection.
An important requirement for successful exploitation is that the integrated CODE server must be stopped (e.g. after a reboot, an upgrade or a crash). No authentication or user interaction is required.
System administrators affected by malicious activity Attacks against multiple endpoints have been reported is from September 10th.
According to the reports, the attacker injected PHP webshells and used them to search for password databases, password manager artifacts and cryptocurrency wallets.
Some users also reported this Ransomware operators exploit the vulnerabilitybut BleepingComputer could not independently confirm this.
System administrators are recommended to upgrade to version 26.4.303 or later or remove the Server app if it is not needed. The provider warned that deactivating the app was not enough.
Beyond the caregivers’ warnings from mid-September, a Community warning was also released on October 3rd, prompting administrators to immediately update due to ongoing exploitation.
However, the lack of a CVE ID made it more difficult for administrators to properly locate the problem and implement effective mitigations.
A study from cybersecurity company Second Security illustrates the gap between security fixes and formal vulnerability notifications.
The company analyzed real-world examples of open source bugs and found that the median time between public fixes and CVE release was 39 days in August, up from 5.1 days in January.
The researchers suspect that increasing volumes of AI-powered vulnerability discoveries are straining CVE processing and contributing to publication delays.
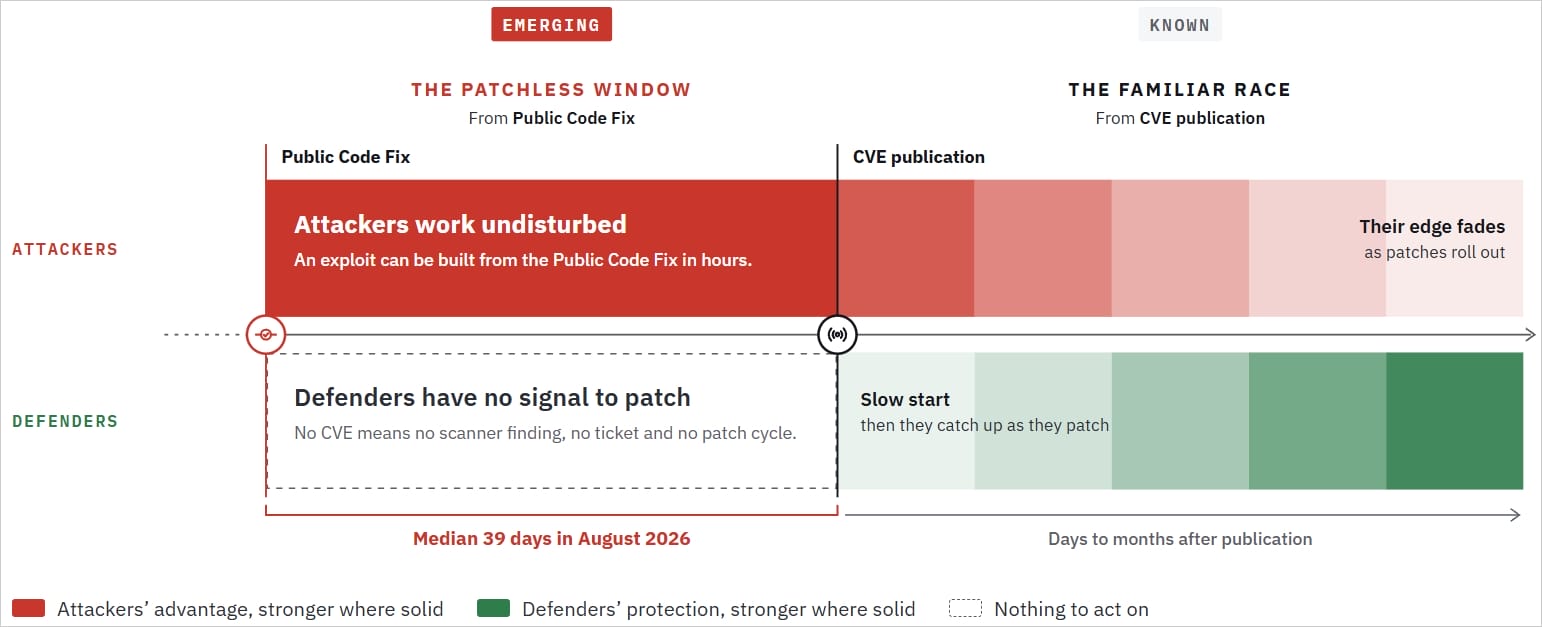
In many cases, researchers found that public exploit code appeared online within hours of a security fix and several days before the corresponding CVE was published.
Second Security notes that the use of AI tools makes it easier for attackers to generate working exploits for published fixes.
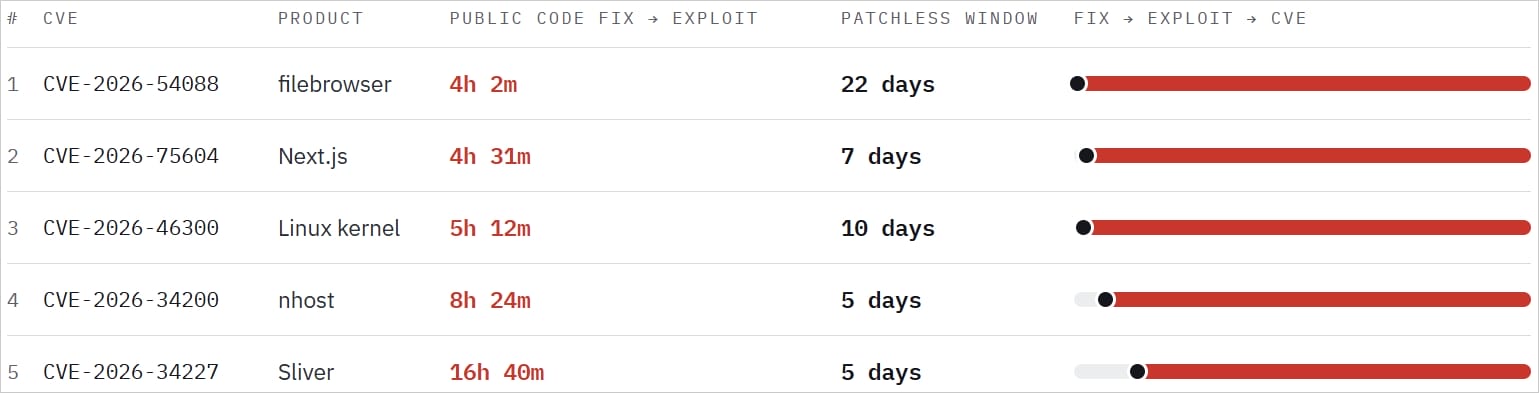
Source: Second Security
In the case of Collabora, the fix was committed on September 9th and version 26.4.303 was released on September 11th. The advisory and CVE were released on October 14, a gap of more than four weeks.
BleepingComputer contacted Nextcloud with questions about its response to the reports of malicious activity, as well as details about the attacks and the number of systems affected.
Nextcloud told BleepingComputer that Collabora reported the vulnerability in mid-September and that an update had become available via the App Store.
The company justified the delay in disclosure by saying it gave users time to update and did not observe widespread exploitation.
In one Blog post Collabora attributed today’s delayed announcement regarding activity primarily to backlogs in GitHub’s CVE processing, which it said was under pressure from the increasing volume of AI-driven security reports.


