
A joint law enforcement agency warns that North Korean hacker group WaterPlum compromised at least 30,000 devices worldwide and transferred more than $10.7 million in stolen cryptocurrency to North Korea from December 2025 to July 2026.
The figures come from a joint consultation by Japanese, US, AustralianAnd German Authorities that jointly tracked the threat group’s activities.
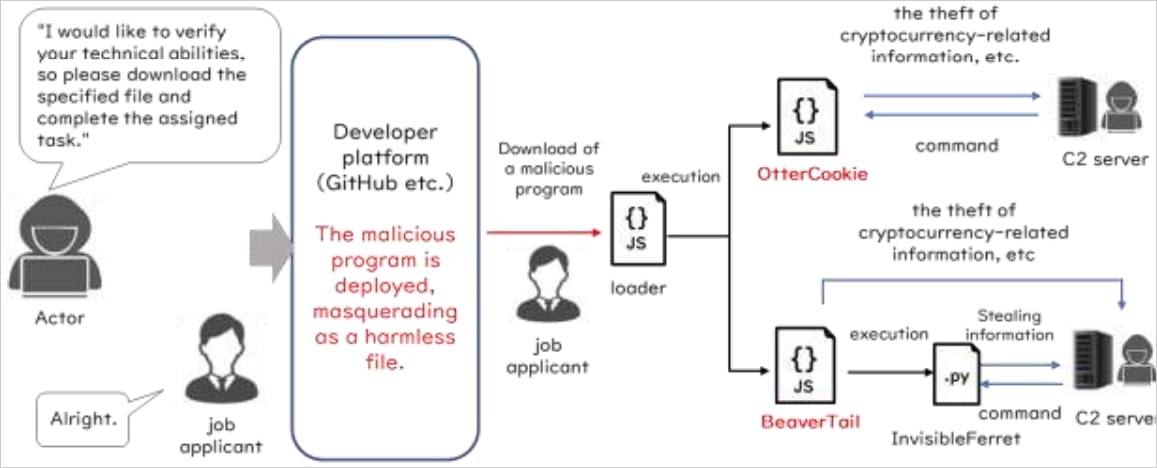
WaterPlum is associated with a multi-year campaign called “Contagious Interview,” which previously targeted job seekers with malicious NPM packages that infected their devices with malware.
The attackers pose as legitimate AI, cryptocurrency and NFT companies or use recruiting and freelance platforms to target job seekers.
In fake interviews and coding tests, victims are instructed to download projects, troubleshoot supposed video conferencing problems, or execute malicious code.
WaterPlum is part of a broader ecosystem of North Korean threat actors carrying out financially motivated attacks to generate revenue for the regime and help fund its weapons programs.
“WaterPlum actors infected at least 30,000 devices in more than 100 countries and exfiltrated funds or account information from over 7,000 cryptocurrency wallets.” reads the guide.
“WaterPlum actors have transferred 1.7 billion Japanese yen (JPY) (equivalent to $10.71 million) in cryptocurrency assets to the Democratic People’s Republic of Korea (DPRK).”
The advisory links several malware families to WaterPlum operations, including:
- BeaverTail: JavaScript malware hidden in NPM packages.
- Invisible Ferret: Python based backdoor.
- OtterCookie: JavaScript remote access Trojans and information theft.
- OtterCandy: Malware that combines OtterCookie and RAT functions.
- StoatWaffle: Modular Node.js malware distributed via malicious Visual Studio Code projects that uses configuration files that execute code after a folder is open and trusted.
Once a target is compromised, attackers attempt to steal browser credentials, clipboard contents, keystrokes, private keys and cryptocurrency seed phrases, and documents while capturing screenshots.
They may also use access to infected computers to break into their employers’ or customers’ networks, expanding attacks to include intellectual property theft and espionage.
Authorities also directly link WaterPlum to North Korea’s fraudulent IT staff operations, saying that some WaterPlum hackers also work as remote IT workers doing web development for clients and that the two groups used the same IP addresses.
The alert also warns that North Korean IT employees are reusing identification documents stolen in WaterPlum attacks to impersonate victims and get jobs.
Investigators also found that WaterPlum cast members used AI software to swap faces during online interviews, then turned off their cameras and blamed network problems.
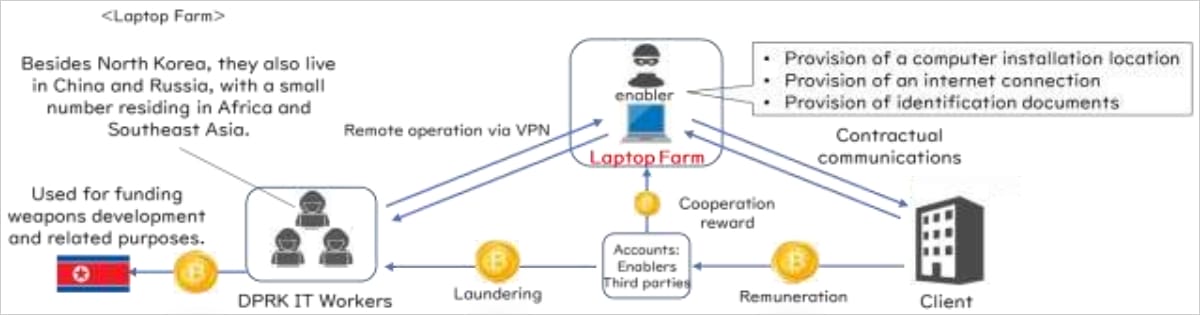
The FBI and Japanese police believe that WaterPlum actors and some North Korean IT employees report to the country’s General Office 313, which is part of the Munitions Industry Division and is responsible for North Korea’s weapons research and production.
According to Japan’s National Police, authorities have identified, investigated and dismantled a “laptop farm” run by North Korean IT workers in the country for the first time, finding evidence that hundreds of millions of yen were being transferred abroad.
The advisory calls on companies to carefully verify the identity, location and qualifications of applicants and to limit their access only to the systems and data necessary to perform their jobs.
Developers should avoid running unknown code outside of a sandbox and check deployed files and code for commands that retrieve additional payloads.



