
An international law enforcement operation dubbed “Operation KillSwitch” seized the KillSec ransomware gang’s data leak site and servers, led to three arrests and identified a 16-year-old as the group’s suspected administrator.
The coordinated law enforcement operation was carried out on September 30, involving authorities from Belgium, the United States, Finland, Germany, Greece, the Netherlands, Romania, Spain, Switzerland and the United Kingdom.
Europol and Eurojust as well as cybersecurity companies Bitdefender and Group-IB also took part in the investigation.
“The action was part of Operation KillSwitch, an international investigation led by German authorities into around 1,000 suspected attacks worldwide,” says Europol.
“Investigators identified a 16-year-old as the suspected key player in the group. Three suspects were provisionally arrested and eight properties were searched in Greece, Romania, Spain and the United Kingdom. Authorities also targeted the group’s criminal proceeds.”
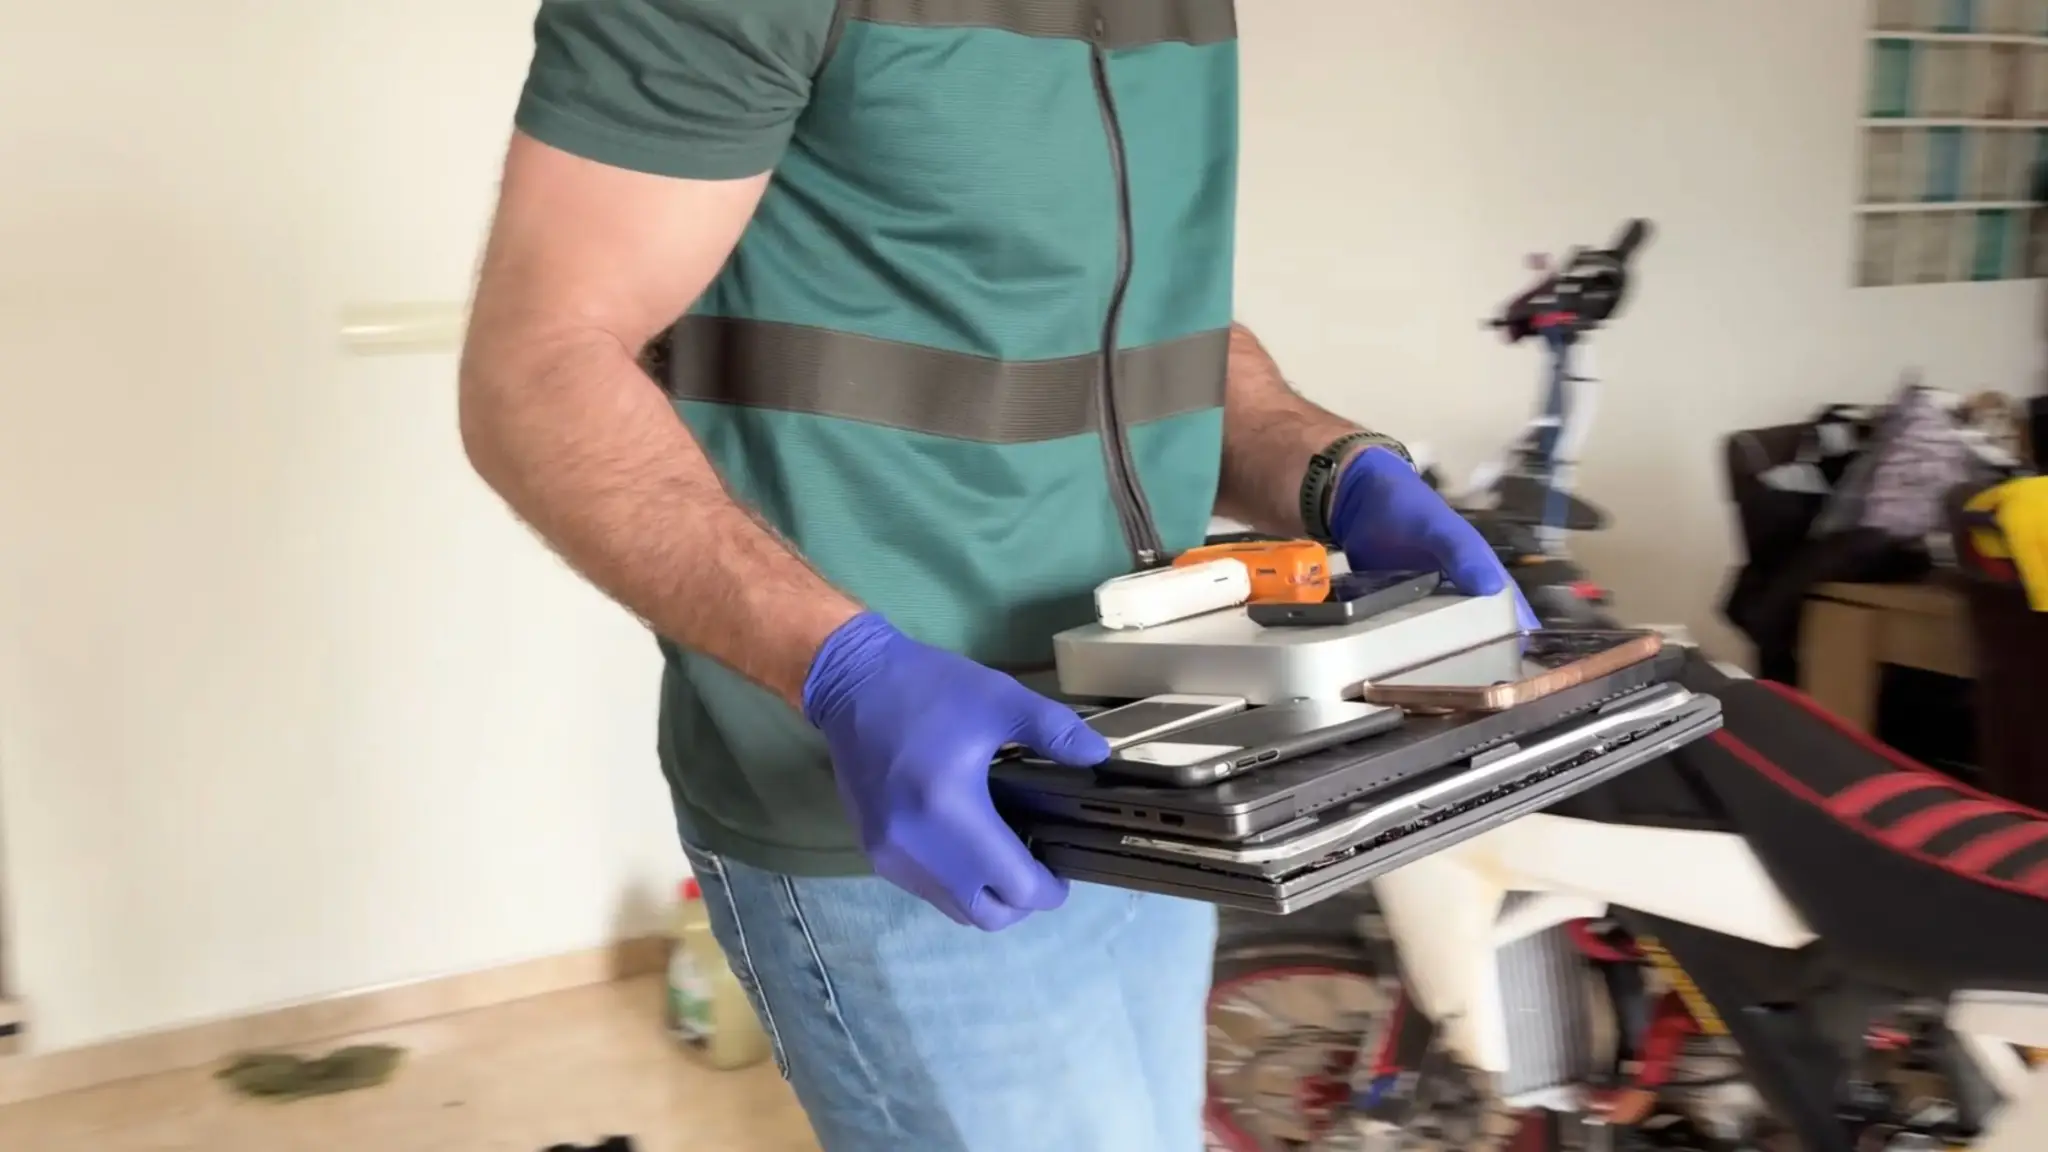
The investigation began in 2025 and helped law enforcement identify suspects believed to be administrators, developers, negotiators and affiliates of the cybercrime group.
According to Europol, the alleged administrator and main operator of KillSec is only 16 years old. Another alleged member, described as a developer, turned 18 in August 2026 and was still a minor when some of the alleged crimes were committed.
Authorities have also identified people suspected of being negotiators and partners.
This was announced by the Hamburg police it examined the group This led to the identification and shutdown of five servers, including KillSec’s main server and several servers that were allegedly used to store stolen data.
One of the seized websites is the KillSec dark web data leak website, hosted at https://ks5424y3wpr5zlug5c7i6svvxweinhbdcqcfnptkfcutrncfazzgz5id.onion/, which now contains a seizure notice.
“The domain, the servers and all associated data in connection with Operation KillSwitch were brought under control by the Hamburg State Criminal Police Office and international law enforcement authorities,” the seizure banner says.
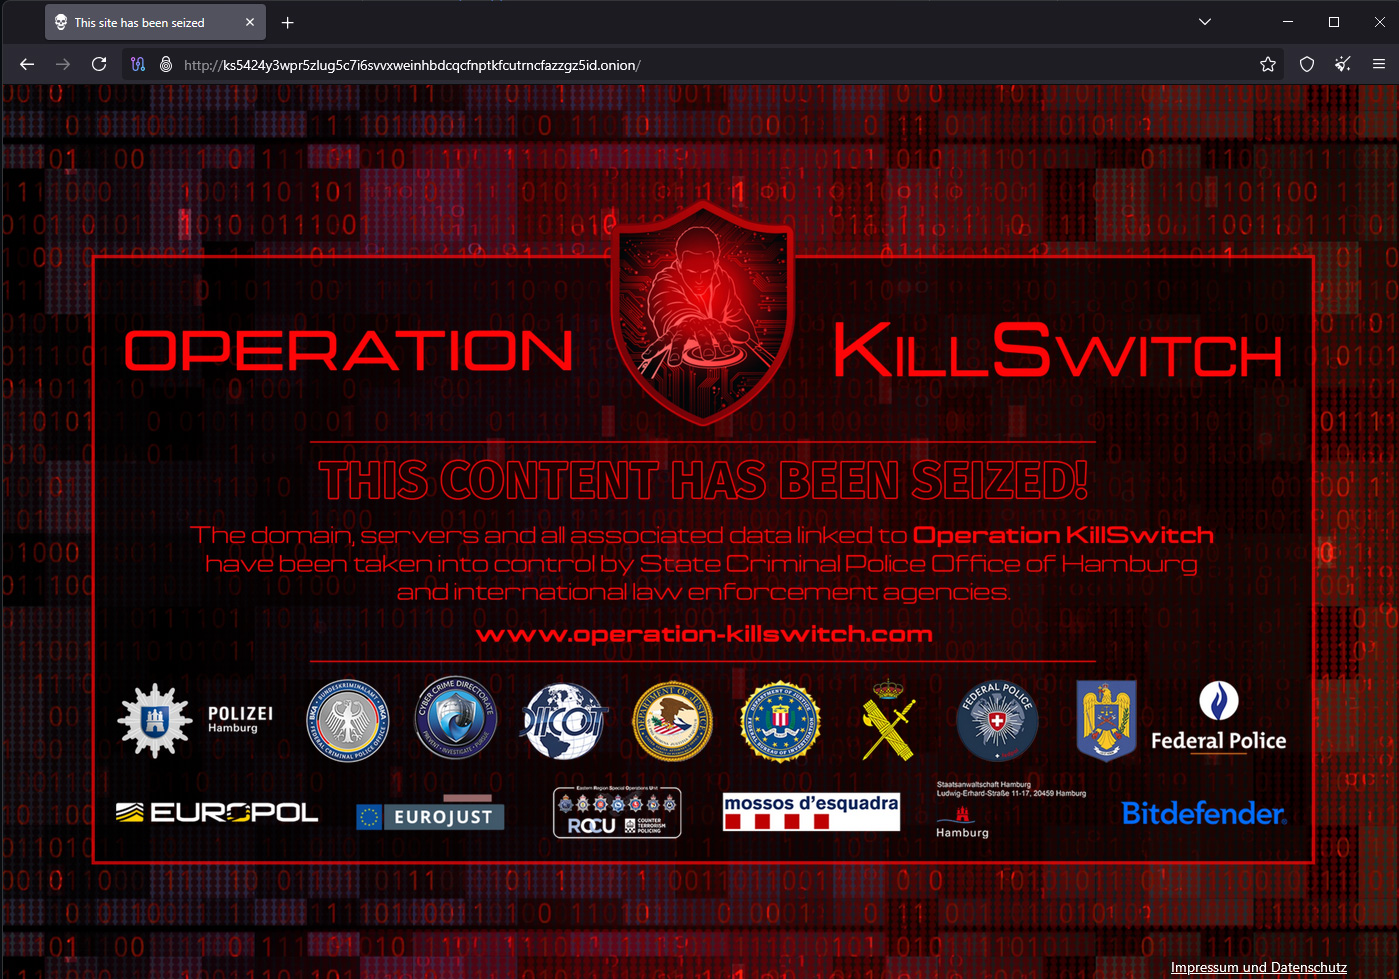
Source: BleepingComputer
Clicking on the confiscation banner leads to Operation KillSwitch Website that features law enforcement video about the ransomware gang and the arrests.
During the operation, law enforcement also seized at least 110 terabytes of stolen data to prevent further unauthorized access, conducted eight searches in Greece, Romania, Spain and the United Kingdom, and made preliminary arrests of three suspects.
So far, investigators have determined that about 500 of KillSec’s attacks have been successful. But authorities warned that the numbers could change as they further analyze the seized evidence.
At least 70 of the suspected attacks are related to organizations in Germany, including 18 cases related to Hamburg.
Active since around 2024, KillSec is accused of exploiting software vulnerabilities and poorly secured edge devices and platforms to break into corporate systems and steal sensitive data.
The threat actors used the stolen corporate data to blackmail victims through the KillSec dark web leak site, with threats that the data would be made public if a ransom was not paid.
According to Europol, KillSec received “significant” ransom payments from these data theft attacks.
Investigators also found that members of the group used artificial intelligence to build and maintain their ransomware infrastructure and identify potential victims.
Authorities are currently investigating seized computers, servers and other data while trying to track down KillSec’s suspected criminal proceeds, including cryptocurrencies.
Investigators believe the seized evidence could reveal additional victims, attacks and people involved in the ransomware operation.


