
BeyondTrust warned customers on Thursday to fix a critical flaw in its Remote Support (RS) that has been exploited in zero-day attacks since late August.
Remote Support is the company’s enterprise-wide support solution that helps IT service desks, help desks and customer support teams resolve issues remotely.
Tracked as CVE-2026-102764actively exploited this Authentication bypass The vulnerability allows unprivileged remote attackers to perform file operations on unpatched appliances and affects RS 26.2.3 or earlier. BeyondTrust fixed the security issue on October 8 for all Remote Support and Privileged Remote Access SaaS customers. However, self-hosted installations must be manually patched if automatic updates are not enabled.
While the company shared limited details about the vulnerability, it said the zero-day was abused in the wild by a suspected China Nexus espionage actor, tracked by Mandiant and security researchers at Google Threat Intelligence Group (GTIG) as “Armory Castle” (formerly UNC5221) and by cybersecurity firm CrowdStrike as “Warp Panda.”
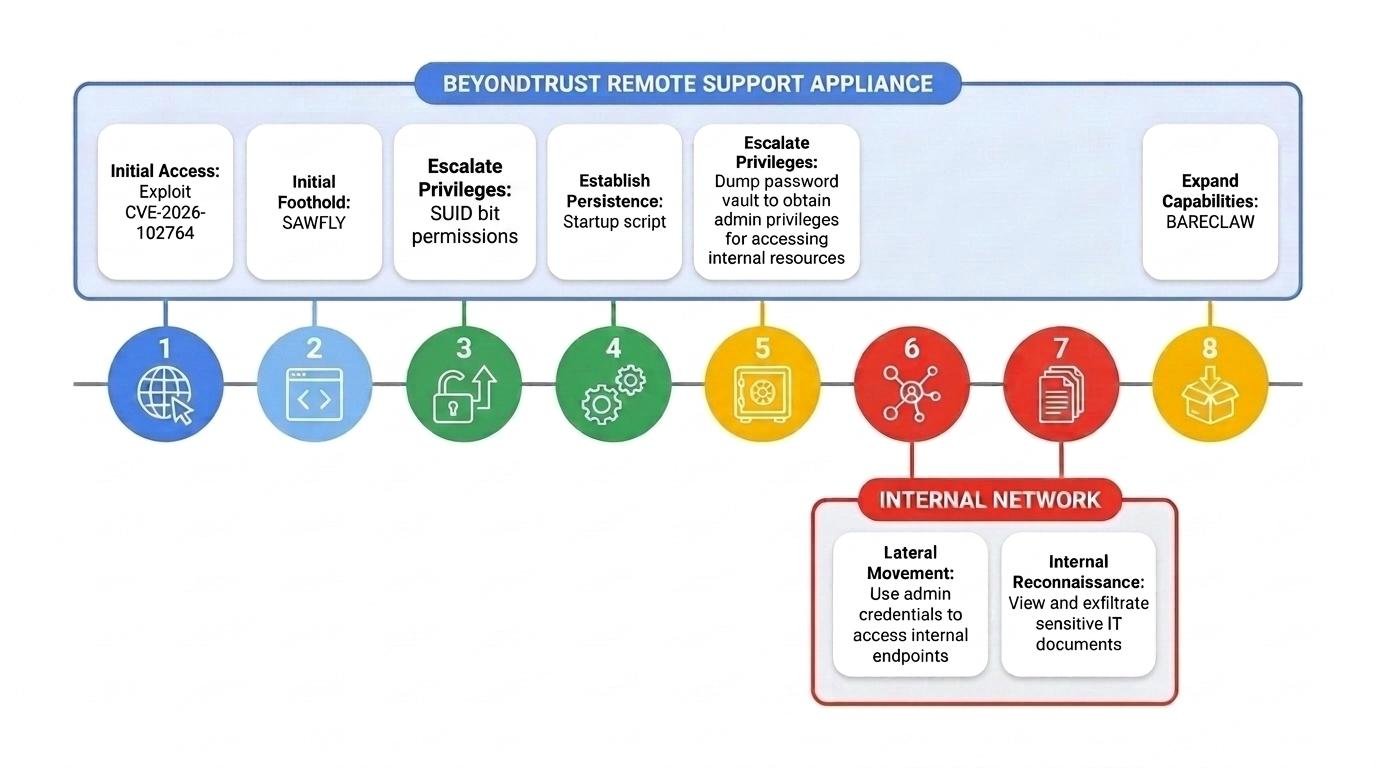
According to Mandiant researchers who discovered the initial attacks, Armory Castle hackers exploited the vulnerability to gain initial access and escalated it to root privileges on compromised devices by enabling Set User ID (SUID) permissions.
Next, they deployed the new Sawfly web shell and Bareclaw Tunneler malware, dropped logs to avoid detection, and moved laterally through the victim’s network using compromised administrator credentials by opening remote sessions on downstream systems.
“After gaining a foothold through the web shell, the actor ascended from the web service account to root-level control of the appliance host. This gave them access to all credentials that the appliance stored or conveyed and the ability to modify files that survive a reboot and configuration reset.” Mandiant said.
“Any appliance that was accessible over the Internet with a vulnerable version during the exploit window should be treated as potentially vulnerable pending review.”
Internet threat monitor Shadowserver Tracks over 1,400 BeyondTrust Remote Support instances However, there is no information about how many of these have already been secured or are honeypots.
Armory Castle is known for combating zero-day vulnerabilities in network edge appliances, including various Citrix NetScalers (CVE-2023-4966) and Ivanti Connect Secure (CVE-2023-46805 and CVE-2024-21887, then CVE-2025-0282) appliances, since at least October 2023, to penetrate corporate networks and spread new custom malware.
Threat intelligence firm Volexity also said in January 2024 that UNC5221 had compromised more than 2,100 Ivanti appliances using the GiftedVisitor webshell in attacks that chained the zero-day attacks CVE-2023-46805 and CVE-2024-21887.
“In previous campaigns, ARMORY CASTLE has conducted wide-ranging and opportunistic attacks following the public disclosure of vulnerabilities that it had selectively exploited as zero-days, attempting to infiltrate target organizations before deploying patches,” Mandiant added. “It is possible that we will see similar widespread exploitation attempts associated with CVE-2026-102764.”
CVE-2026-102764 is the latest in a series of other BeyondTrust vulnerabilities that threat actors have exploited in recent years. Most recently, attackers exploited another critical remote code execution vulnerability (CVE-2026-1731) affecting Remote Support and Privileged Remote Access appliances to establish WebSocket channels and deploy ransomware.
The The Chinese state-backed hacker group Silk Typhoon The company is also believed to have exploited two zero-day attacks (CVE-2024-12356 and CVE-2024-12686) to penetrate BeyondTrust’s systems and use a stolen API key to compromise 17 Remote Support SaaS instances, including the US Treasury Department instance.
In the same campaign, Silk Typhoon also targeted the Office of Foreign Assets Control (OFAC), which manages US sanctions programs, and the Committee on Foreign Investment in the United States (CFIUS), which reviews foreign investments for national security risks.
BeyondTrust provides identity security services to over 20,000 customers worldwide, including government agencies and 75% of the Fortune 100 companies.


