
The third-party.com domain, commonly used as a placeholder in developer documentation and code samples, provides a fake Cloudflare verification page that attempts to trick Windows users into running PowerShell commands.
The third-party.com domain has long been used in documentation to represent any external website, API, or service, similar to how developers use domains like example.com.
However, unlike example.com, example.net and example.org, which IANA reserves specifically for documentation, third-party.com is a typically registered domain whose content the owner can control.
This difference now poses a security risk after the domain launched a ClickFix attack that spoofed a Cloudflare security review.
Manifold Security first reported the malicious use of the domain after it was discovered while examining public AI capabilities and MCP server documentation that referenced the domain.
BleepingComputer has since confirmed that the site displays a fake Cloudflare CAPTCHA “Security verification in progress” screen with a prompt to “Confirm you are human.”
After the user clicks the confirmation box, the site copies a malicious PowerShell command to the Windows clipboard and then instructs the user to press Windows Key + R, paste the contents of their clipboard with Ctrl+V, and press Enter.
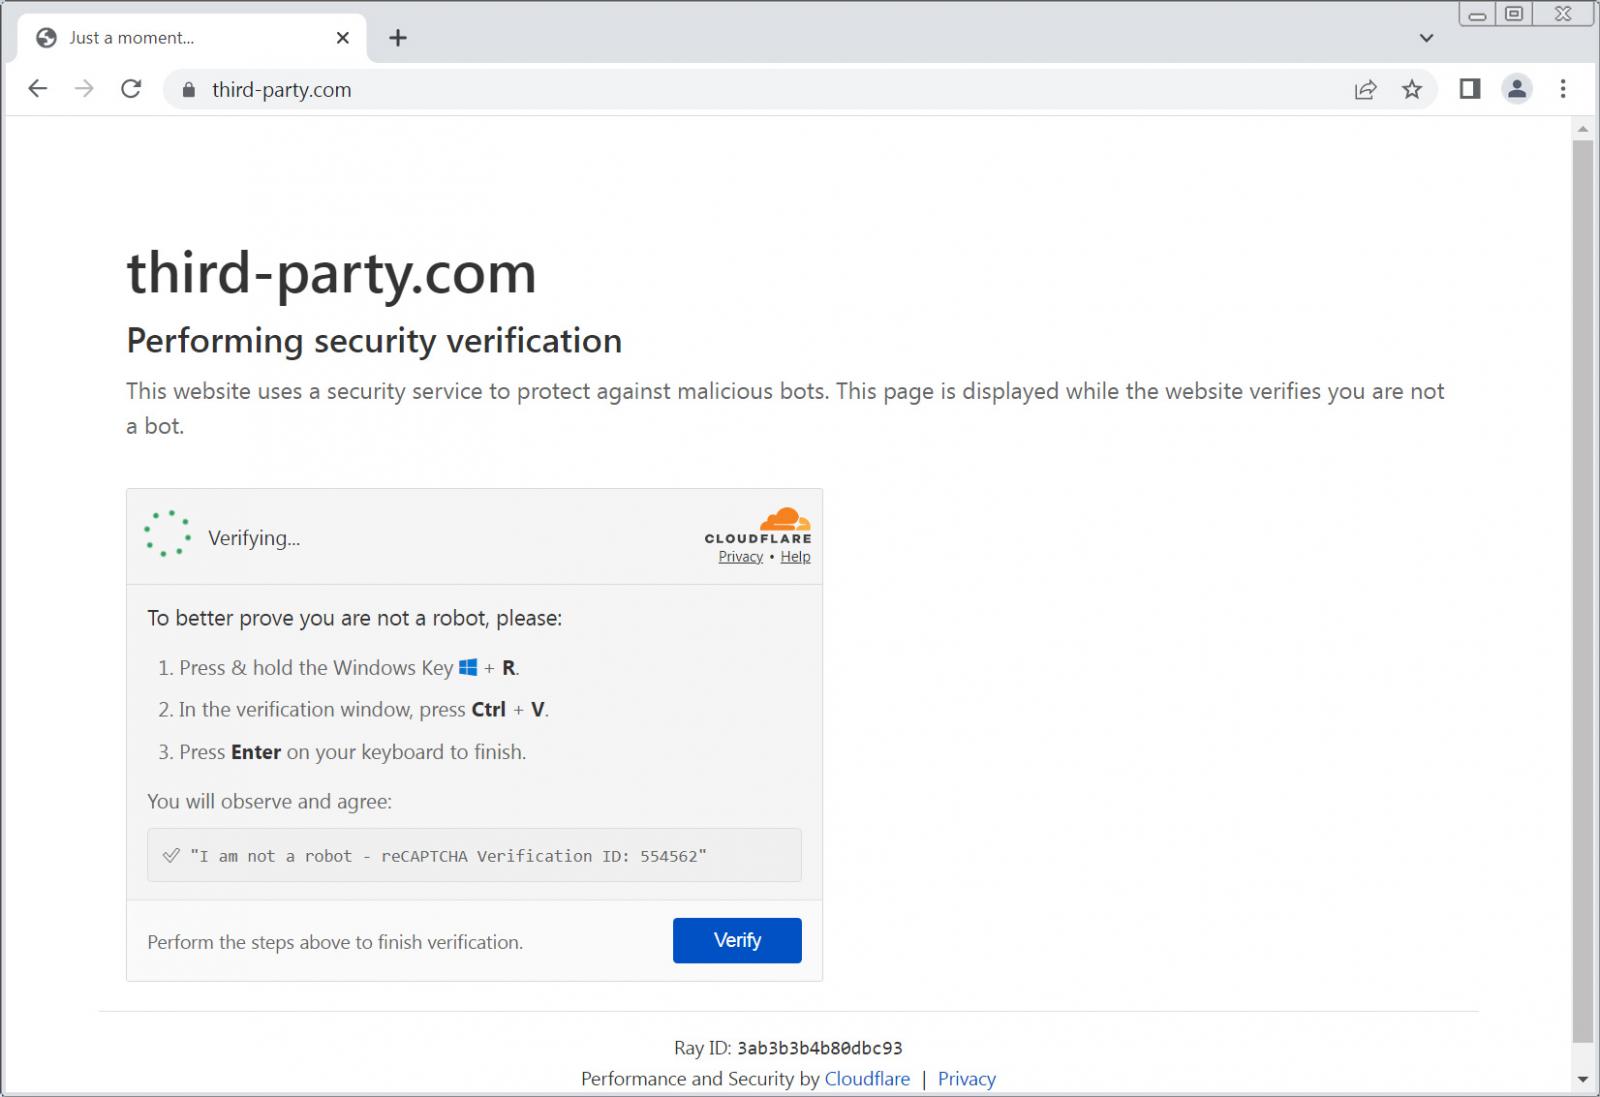
Source: BleepingComputer
When the PowerShell command is executed, the payload URL is reconstructed elxxvvx(.)xyz/f, downloads a PowerShell script from this address and then runs it.
This technique is commonly known as ClickFix, where attackers use fake errors, CAPTCHA prompts, or verification pages to trick victims into manually executing commands copied to their clipboard.
ClickFix attacks have become a popular method of spreading malware because the malware is installed via user-executed commands rather than downloaded from websites or as email attachments. In some cases, this could allow malware to be installed while bypassing traditional antivirus software.
At the time of BleepingComputer’s testing, elxxvvx(.)xyz was no longer resolving, breaking the current attack chain.
However a Hybrid Analysis Report dated May 2, 2026 shows that the site has distributed a PowerShell script configured to download a 134MB zip archive from:
https://elxxvvx(.)xyz/update2.zipThe PowerShell script saved the archive as update26.zip, extracted it, and then attempted to launch an executable called draw.io.exe.
Because the update2.zip archive is no longer available, BleepingComputer was unable to determine what the payload does.
Manifold’s Ax Sharma says the attack specifically targets Windows users, with Linux and Mac visitors receiving error messages indicating that their operating system is not supported.
“A macOS or Linux user agent doesn’t get any of this. It gets a nearly identical page that stops on an error: “macOS is not supported.” A Windows PC is required to access this website. “No clipboard poisoning, no payload,” explains Sharma.
“The attacker only shows the weapon to the targets it is effective against, which is precisely why a cursory glance or scanner on a Linux data center IP will not detect anything wrong.”
A placeholder that was not reserved
The more interesting aspect of the attack is the domain Third-Party.com, which was chosen to host the ClickFix page.
Public developer documentation has treated Third-Party.com as a generic example hostname for many years.
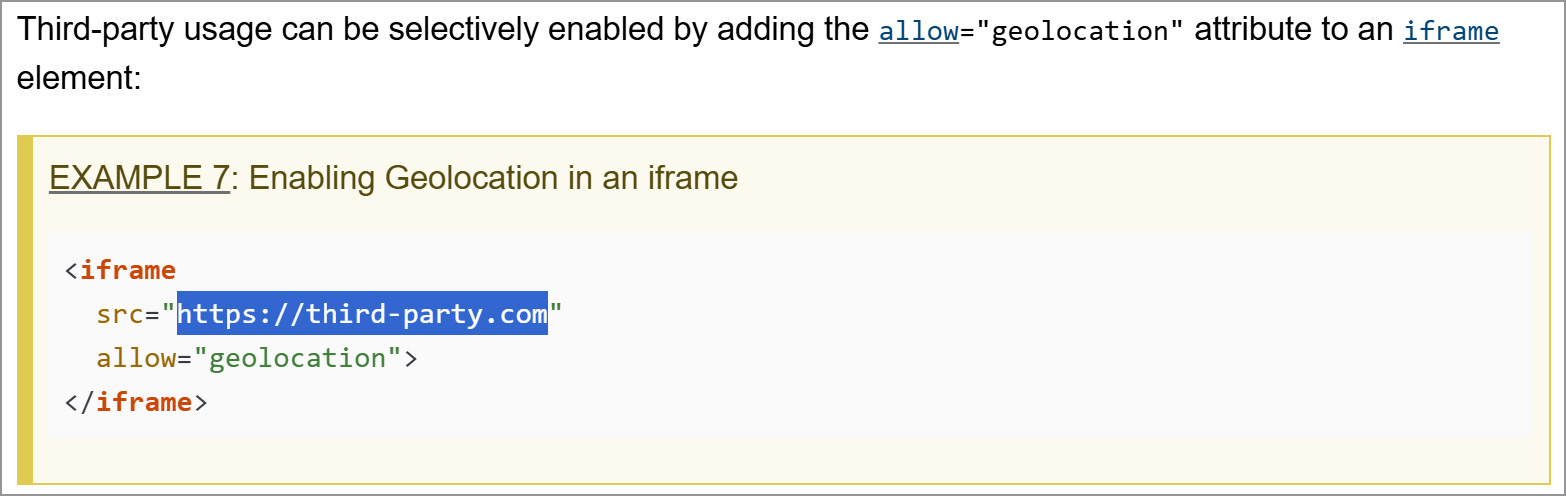
For example this W3C geolocation specification Currently shows granting geolocation permissions to an external iframe using third-party.com as a wildcard domain:
The W3C Compute Pressure specification Similarly, the domain is used when demonstrating how a website can enable the Remote Content API:
Chromium’s documentation on this Telemetry extension API also uses third-party.com as an example website that is allowed to communicate with a Chrome extension:
Other examples go even further and use the domain in code that, if copied verbatim, would actually make network requests.
A PrivacyCG proposal on GitHub also uses the domain as the target of a JavaScript fetch() request from a service worker.
Posts online indicate that developers have copied these and similar examples into their own code and projects.
In one Stack Overflow 2015 questionA developer said he applied an asynchronous loading example using https://third-party.com/resource.js to his website before realizing that it didn’t behave as expected after publishing the website.
These examples do not mean that the associated projects or documentation are at risk.
However, applications or test code that copied such placeholder URLs could now cause a browser or automated tool to contact the real Third-Party.com domain, potentially displaying the ClickFix attack in a browser or application.
Unlike example.com, which is maintained by IANA for documentation purposes and is not permitted to be registered or transferred, the third-party.com domain has no such protection and was clearly hijacked or registered at some point to carry out these ClickFix attacks.
“third-party(.)com has been a general documentation placeholder for years, example.com plays the same role,” explains Manifold.
“A public code search reveals skills, MCP server documents, and over 1,500 files in more than 1,700 repositories from such trusted names as Chromium, Sanity, and Vercel. It has served as a ClickFix lure since at least June 2026.”
Although the widespread use of “third-party.com” as a placeholder in documentation makes the domain attractive to attackers, there is no evidence that it was registered for malicious purposes.
The domain was first registered in 1996, long before the current campaign, and BleepingComputer has not determined when or how control of the site changed.
At this time, there have been no reports that these third-party.com references have actually resulted in ClickFix attacks being executed on developers’ devices or within their applications/websites.
However, since the domain remains active, it could easily be switched to a new live payload domain and actively used in future attacks.


