Security researchers have developed an attack that allows hackers with privileged access to register a rogue third-party MFA provider that steals users’ passwords during legitimate login attempts.
The technique, which Varonis Threat Labs calls TrustSink, can work with any vendor that relies on this external authentication model, although researchers demonstrated the attack using Microsoft Entra.
Microsoft Entra supports third-party MFA providers that enable organizations to leverage third-party authentication services to meet multi-factor authentication requirements.
Accordingly MicrosoftWhen a user logs in with a first factor, such as a password, Entra can redirect them to a third-party MFA provider to complete the required second factor.
If the provider returns a valid signed token indicating that the second factor has been completed, Entra assumes that the MFA requirement has been met.
Varonis has discovered that an attacker who has already compromised a highly privileged Entra account can register a fraudulent external authentication method (EAM) as one of these external MFA providers, thereby injecting a convincing Microsoft password challenge into the legitimate authentication flow.
The fake prompt captures the user’s password in plain text before the malicious provider sends a valid signed token back to Entra, completing the login without displaying an error.
“In our test tenant, every login completed normally, while our server received passwords with timestamps and source IP addresses.” explains Hero.
“Resetting a captured password did not remove the rogue provider. It remained in the authentication flow and captured the replacement password the next time the user logged in.”
It is important to note that TrustSink is not a first-access attack and requires an attacker to already control a highly privileged Entra account.
Abuse of an external MFA provider
TrustSink abuses the trust that Microsoft places in a configured external MFA provider.
Varonis created a malicious provider that appeared to Entra as a legitimate third-party MFA provider, but presented the user with a copy of the Microsoft password page.
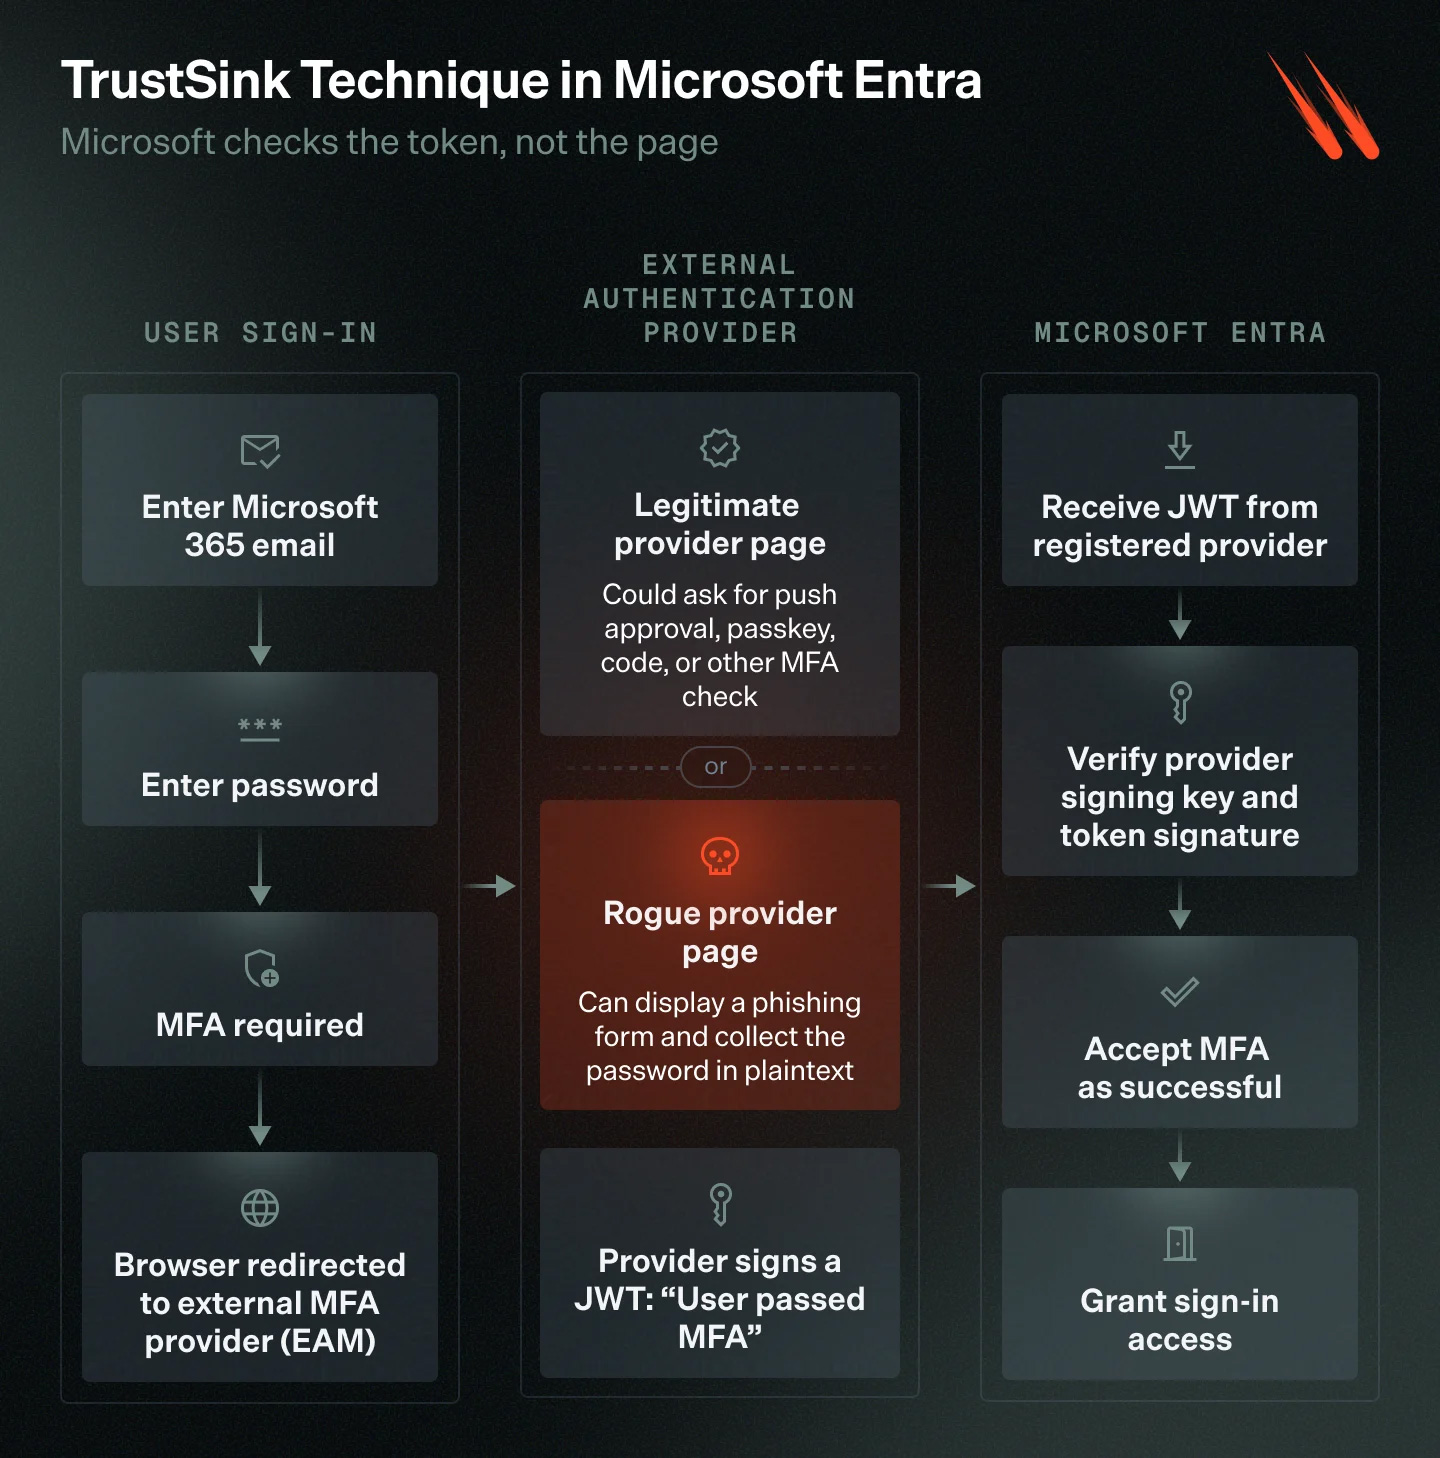
During the proof-of-concept attack, login initially occurs normally, with the user entering their email address and password on Microsoft’s legitimate login.microsoftonline.com website.
When MFA is triggered, Entra redirects the browser to the attacker’s external MFA provider for the second authentication step.
Instead of presenting a legitimate second-factor challenge, the malicious provider displays a copy of Microsoft’s password prompt.
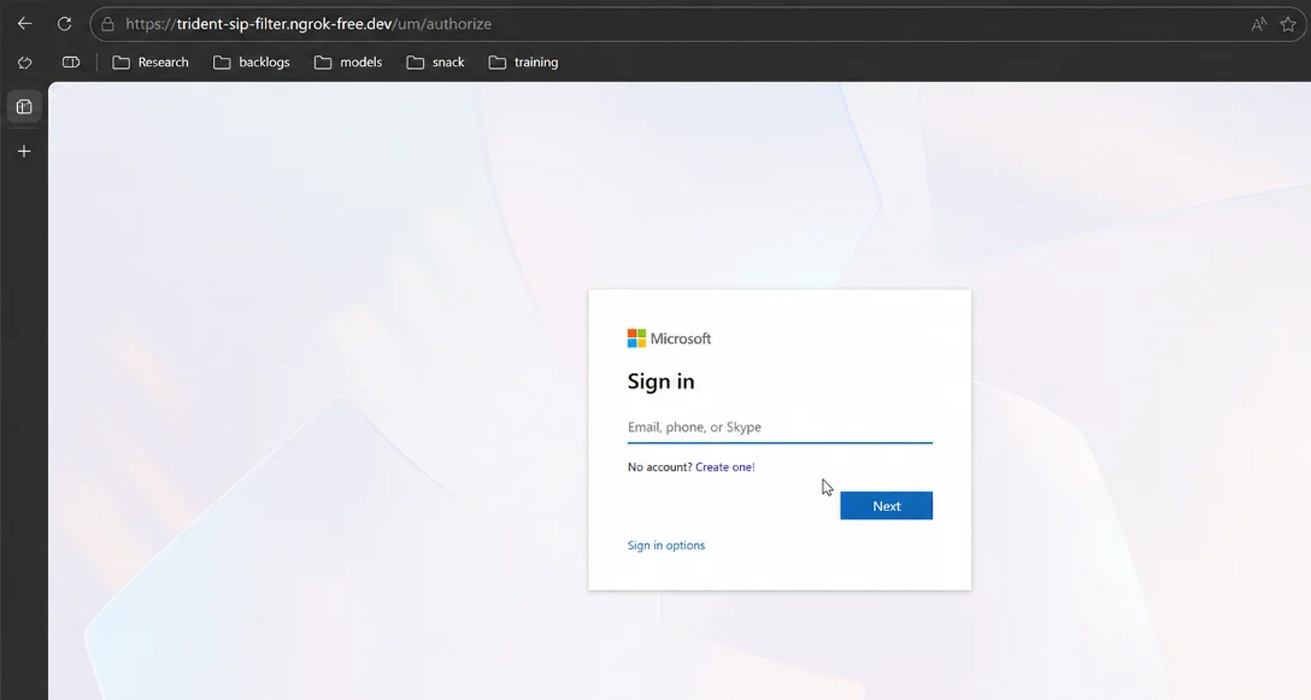
Source: Hero
If the victim re-enters their password believing Microsoft is requesting it as part of the authentication process, the credentials are sent to the attacker-controlled server.
The fraudulent provider then generates a signed token indicating that the MFA prompt has completed and sends it back to Entra, allowing the user to continue with the application they originally intended to access.
From the victim’s perspective, the registration appears to have been completed normally.
Varonis says the attack is convincing because the spoofed password prompt appears when the user is already expecting another authentication step.
Researchers say the page uses the same fonts, layout and button design as Microsoft’s legitimate login page and appears immediately after the victim enters their real password on Microsoft’s domain.
Varonis says TrustSink builds on previous research by security researcher Dirk-Jan Mollema, presented at x33fcon 2025 in a talk titled “ “Bring your own identity to Entra ID.”
Mollema showed how a fraudulently registered third-party MFA provider could fulfill an MFA request by sending back a signed JWT and claiming that the authentication was successful without actually performing the expected authentication check.
TrustSink abuses the same attack to steal credentials.
According to Varonis, registering the malicious external method requires a change to the authentication methods policy, as well as the creation of an application, service principal, and consent grant.
These actions require a global administrator or authentication policy administrator account, making TrustSink a post-compromise technique.
However, once installed, the rogue provider may remain in the authentication path for targeted users during subsequent logins.
Because the fraudulent MFA provider remains registered in the tenant’s authentication method policy, it will be re-accounted for on the next login attempt, even if a user changes their password.
Varonis therefore warns administrators to remove the malicious provider before replacing the affected credentials.
Varonis recommends removing suspicious third-party MFA providers and their associated applications, keys, and redirect URIs before resetting affected users’ passwords.
Organizations should also monitor changes to authentication method policy, restrict global administrator and authentication policy administrator rights, and use phishing-resistant authentication methods such as FIDO2 or Windows Hello for Business.



