According to a new report from Google Threat Intelligence Group (GTIG), the number of vulnerabilities disclosed each month doubled in 2026, and the monthly average of vulnerabilities exploited in the wild nearly doubled.
Analyzing disclosures from January 2025 to August 2026, GTIG found that monthly disclosures increased from 5,045 in January 2026 to 10,477 in July and peaked at 10,740 in August.
“We have found that AI is measurably changing not only the pace of vulnerability discovery and exploitation, but also the types and typical risk profiles of the vulnerabilities discovered,” says GTIG.
The researchers warn that raw volume can be misleading as automated CVE allocation in open source ecosystems can inflate the numbers. Vulnerabilities whose description mentions the Linux kernel alone resulted in approximately 5,000 CVEs between January and August, with no zero-day exploit observed in the wild.
High-risk disclosures, which are based on GTIG’s own ratings rather than CVSS, rose 167%, from 131 in January to 350 in August. Additionally, GTIG recorded 141 uniquely exploited vulnerabilities in the first eight months of 2026, more than the 127 in all of 2025. That’s an average of 18 per month, up from 10.5 last year.
Still, only 0.23% of vulnerabilities disclosed this year, about one in 431, were exploited.
Zero-day exploitation increased only slightly, from an average of eight per month in 2025 to 11 per month in 2026, although the number rose to 22 in August. Zero-days accounted for 62% of vulnerabilities exploited between January and August.
GTIG assumes that the growth in exploitation is mainly due to n-days. Exploitation of high-risk vulnerabilities also more than doubled, from 28 in 2025 to 75 in the first eight months of 2026.
“It is possible that threat actors may find it more accessible or efficient to use LLMs and AI tools to automate the analysis of differences between product versions, patches, vulnerability disclosure announcements, and proof-of-concept (POC) code to quickly weaponize N-days rather than discovering new zero-days,” the report said.
Vulnerabilities that GTIG identified as likely discovered by AI between January and August have a different risk profile. Of these, 39% were classified as low risk and 58% as medium risk, compared to 69% and 28% for non-AI vulnerabilities, respectively.
According to GTIG, this likely reflects how research programs deploy AI agents and task them with auditing critical infrastructure and sensitive privilege boundaries, with a focus on higher-impact insights.
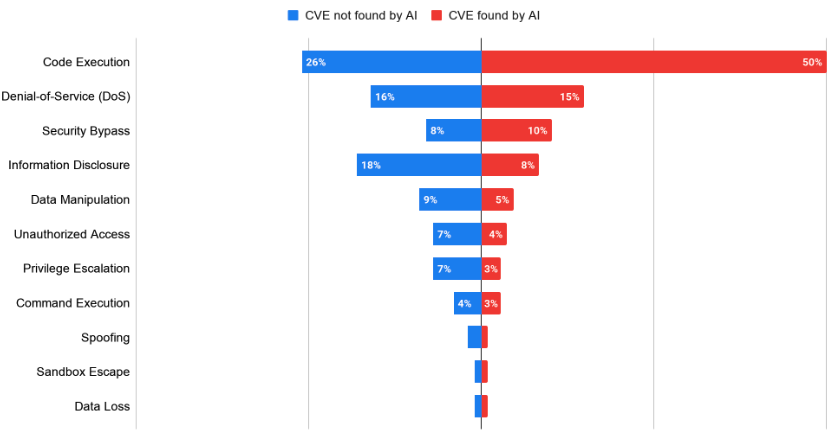
Half of vulnerabilities discovered by AI lead to remote code execution, compared to 26% of non-AI vulnerabilities. According to GTIG, this is likely due to the ability of AI models to find memory corruption and logic errors that traditional static analyzers miss.
GTIG has also confirmed the exploitation of AI-discovered vulnerabilities in the wild, but describes this as an early indicator rather than an established trend.
One example is CVE-2026-1731, an unauthenticated operating system command injection flaw in BeyondTrust Privileged Remote Access and Remote Support that was independently discovered by AI research agent Hacktron. One threat cluster exploited it within four days of release, and five more followed within seven days.
The disclosure of vulnerabilities in AI systems themselves is also increasing. GTIG tracked 2,076 AI-related CVEs between January 2025 and August 2026, including more than 1,500 this year, about half of which involved AI orchestration frameworks.
Only a handful of the 2,076 have been confirmed to have been exploited in the wild, including bugs in LiteLLM and Langflow. GTIG has not yet observed any zero-day exploitation of AI infrastructure.
“GTIG believes that the frequency of discovery and exploitation of vulnerabilities is likely to continue to increase in the short to medium term,” the company said report reads.
Related: Fixed high-level security vulnerabilities in OpenSSL and WolfSSL
Related: WatchGuard fixes a critical code injection vulnerability in the Fireware operating system
Related: Chrome and Firefox updates fix over 100 security vulnerabilities



