Hackers abuse legitimate Bing search result redirects as click-through URLs in Google Search Ads to direct users to fake Claude installers that carry out ClickFix attacks.
The technique, dubbed “Adception” by security researchers at Push Security, appears designed to bypass advertising security checks by using Bing’s trusted domain as an advertising target before redirecting victims to the malicious download page via a compromised website.
The attack also uses multiple layers of stealth to prevent security scanners and visitors who access the malicious URLs directly from seeing the payload.
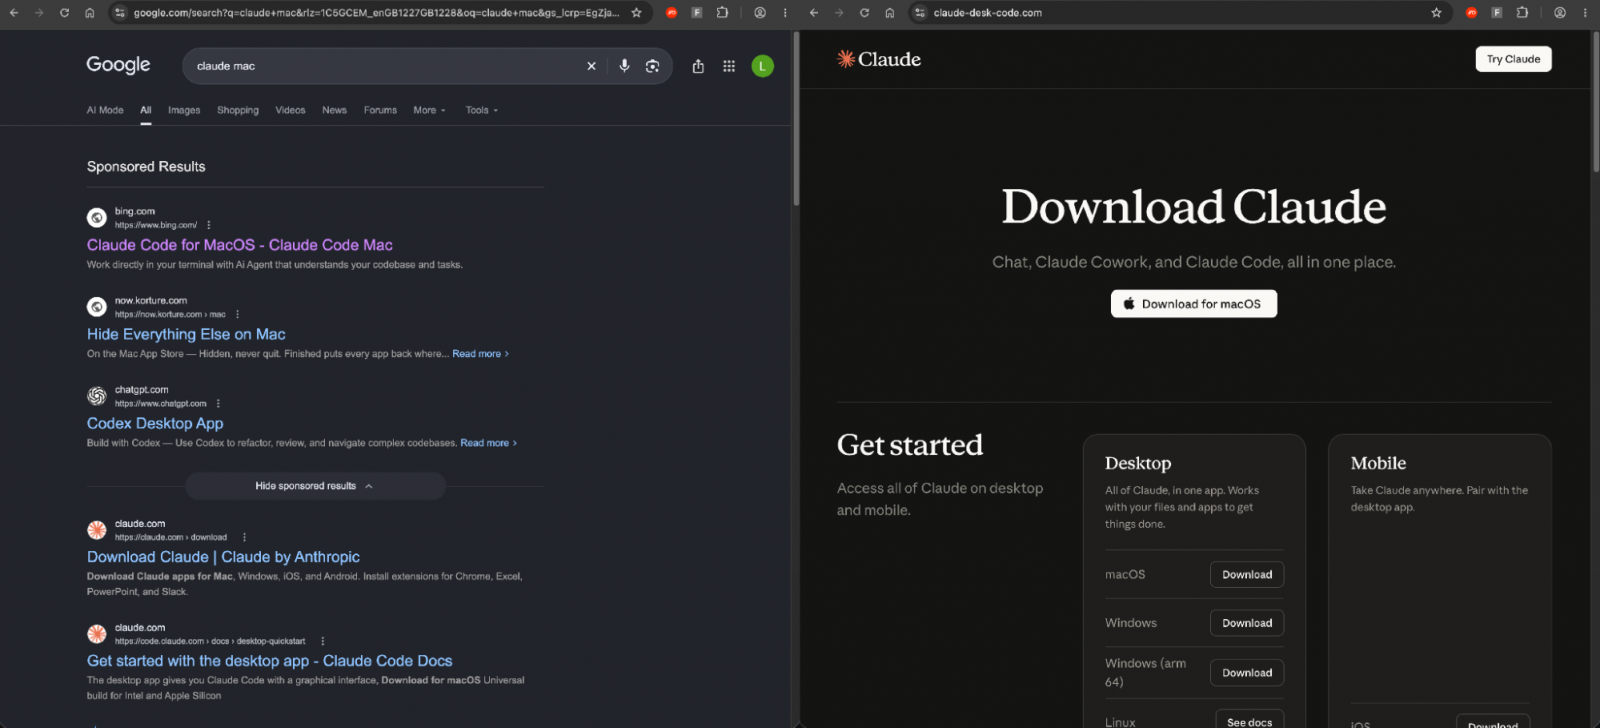
According to a report published by Push securityThe campaign was discovered after researchers discovered a malicious Google ad that targeted users who searched for “Claude Mac.”
Source: Push Security
Unlike typical malvertising campaigns that redirect victims to attacker-controlled domains, the sponsored result displayed the legitimate bing.com domain, making the advertisement appear less suspicious.
When clicked, Push says that the ad first went through Google’s ad redirect before reaching Bing’s bing.com/ck/a Click tracking endpoint that redirected the browser to a legitimate but compromised WordPress website owned by a South American retailer.
The compromised website then redirected the visitor claude-desk-code(.)coma fake Claude download page aimed at tricking macOS users into executing malicious commands.
Bing’s click tracking redirects use JavaScript to direct visitors to their destination. This allows attackers to redirect users to malicious websites while making it appear that the traffic is coming from Bing.
The campaign also uses two layers of stealth to prevent unwanted visitors from reaching the payload.
The compromised WordPress website looks for a Bing referrer and specific browser headers before redirecting visitors, while the fake Claude website uses JavaScript to check whether visitors are coming from Google or Bing.
Visitors who attempt to access the malicious website directly are redirected to a 404 error page, making it more difficult for automated security scanners to analyze the attack.
The fake Claude installer hides malicious commands
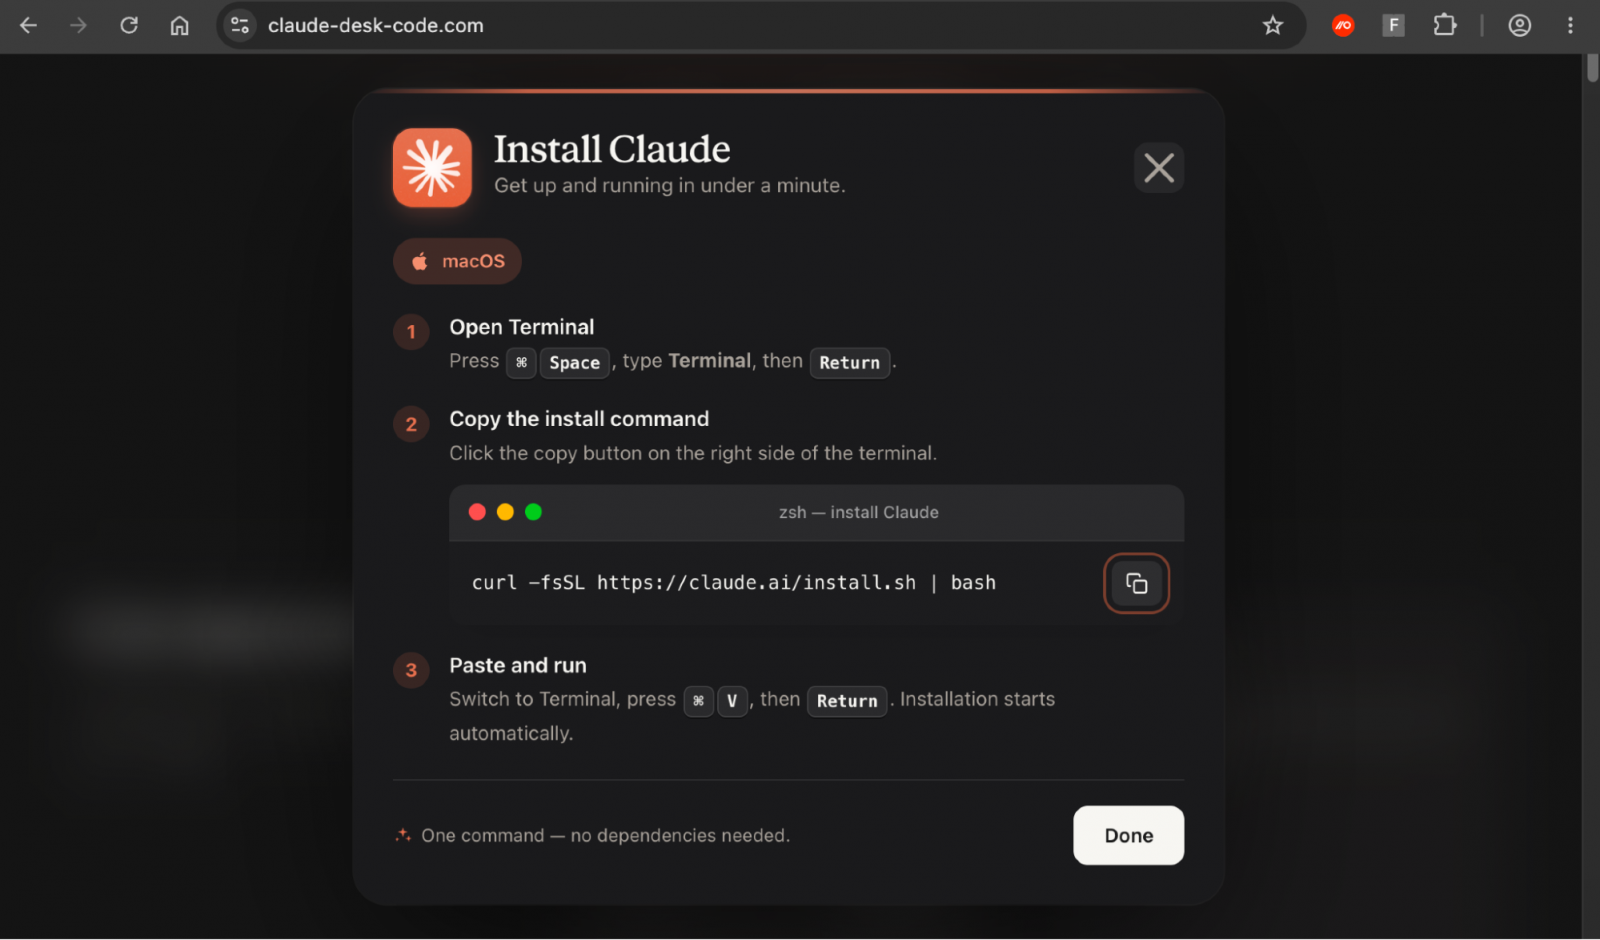
The end goal is a convincing imitation of a Claude download page that offers a macOS installer using an install command typed into the terminal.
Source: Push Security
However, while the page displays Anthropic’s legitimate installation command, curl -fsSL https://claude.ai/install.sh | bashWhen you click the “Copy” button, a malicious command is placed on the clipboard.
The replaced command first prints a message claiming to download Claude from Anthropic’s official website, but actually decodes a Base64 encoded URL pointing to it lake-90(.)com.
It then silently downloads a .dat file from the attacker-controlled server using Curl and passes its contents directly to the macOS Z shell (zsh) for execution.
This means that victims will see the legitimate Claude installation URL on both the download page and in the terminal, despite running a completely different script.
The final payload of the attack remains unknown, making it unclear what, if any, malware will be installed.
According to Push Security, multiple domains associated with the same ClickFix toolkit, tracked internally as AcSig, have been identified and use an identical macOS installation command, payload URL structure, and installation interface.


