A new variant of the MacSync information-stealing malware targeting macOS systems is now using public iCloud calendar events to deliver new payloads.
MacSync is a Swift-based malware that emerged in April 2025 and was recently delivered in ClickFix campaigns under the guise of Homebrew and macOS disk space analysis tools.
Kaspersky researchers say that previous versions of the malware were derived from the AMOS stealer family, but MacSync evolved and added new features via modules.
Supply chain
MacSync was distributed to victims through social engineering, including ClickFix-style attacks, and through software presented as free, cracked, or new applications.
The researchers note that the threat actor deployed the malware as a fake crypto wallet called Toria, which had its own website and was promoted across social media platforms.
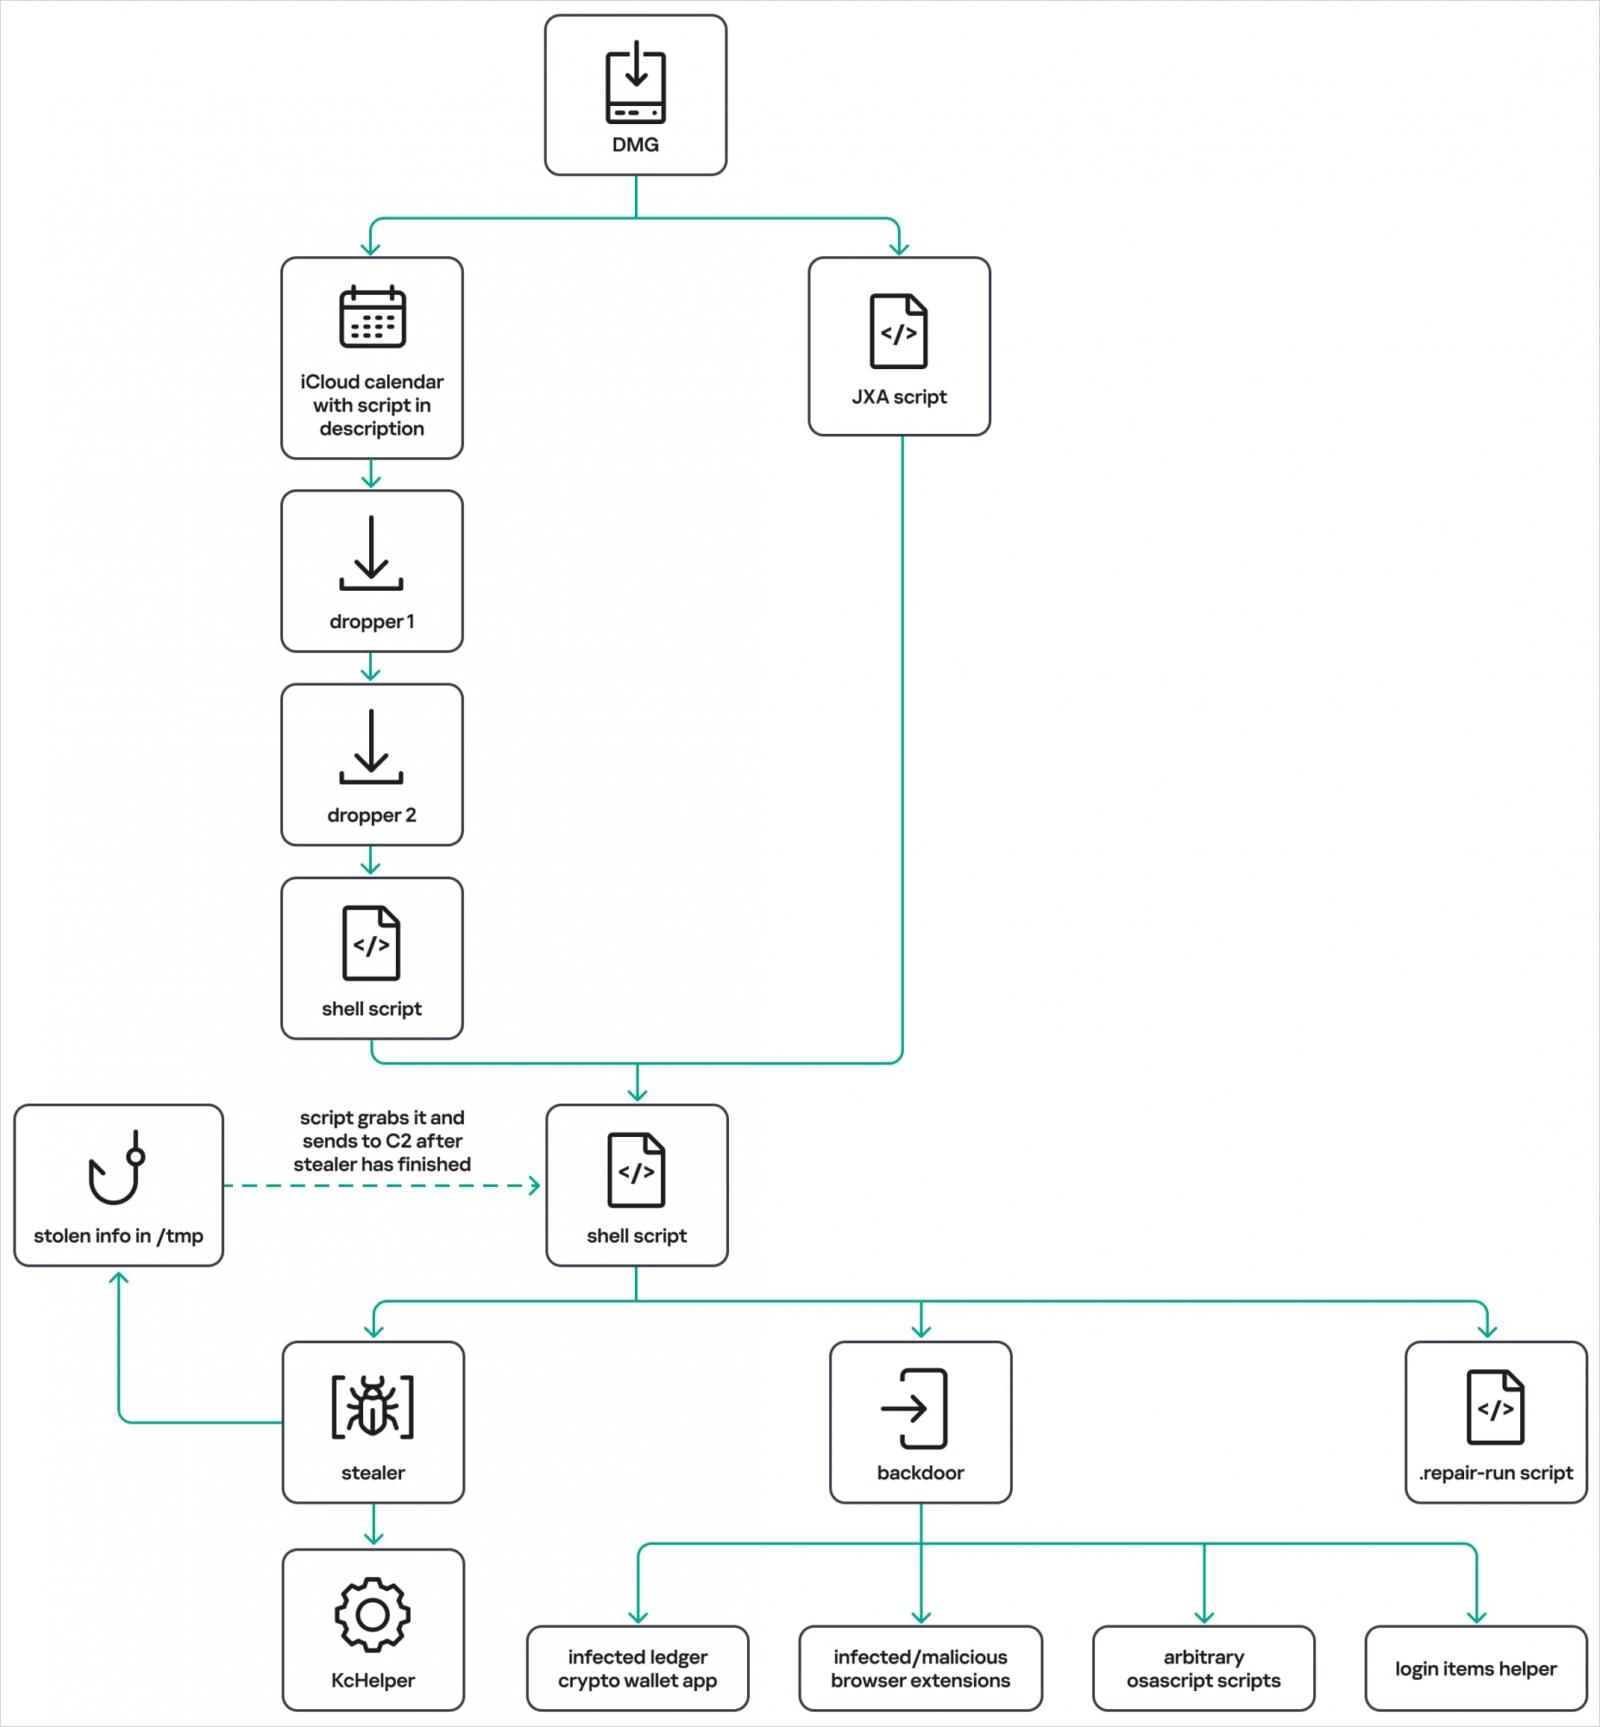
Kaspersky discovered the MacSync campaign, which had two delivery methods. In the more complex variant, a downloader retrieves commands hidden in the description of a public iCloud calendar event and then downloads the next-stage payload from iCloud.
The downloader forwards the retrieved calendar data to the macOS zsh shell. Most of the calendar text will result in errors, but commands placed after the event’s DESCRIPTION: line will run and retrieve an archive of the malware components.
The archive contains an “APP” bundle that acts as a dropper and leads to further stages that ultimately retrieve the MacSync malware.
Source: Kaspersky
New backdoor module
The Infostealer module remains largely unchanged and targets browsing history, cookies and saved credentials, crypto wallet extension and app data, Telegram data, the keychain file, system and device information, SSH, AWS, Kubernetes, Git and shell configuration files.
Source: Kaspersky
The new module observed is an Objective-C backdoor that masquerades as Finder, the default file manager on macOS. Its installer establishes persistence through a LaunchAgent, .zshrc changes, and global Git hooks, while also terminating macOS notification processes to prevent alerts from reaching the user.
The backdoor can perform the following actions on infected systems:
- Execute attacker-provided AppleScript obtained from their command and control server.
- Deploy a browser extension or replace an installed Ledger wallet app with versions provided by the command and control (C2) server.
- Collect additional system information and files and upload them to the C2 server.
- Check persistence and establish it so that it starts again after a reboot.
Kaspersky inferred the purpose of the commands from their names and status messages because the program did not have the AppleScript code that would execute them
The researchers also identified a “mysterious” command: live_browserwhich downloads and runs a component called sn_relaywhose purpose Kaspersky could not determine.
As MacSync continues to evolve and introduce more complex and effective distribution chains, macOS users are advised to avoid executing commands they find online
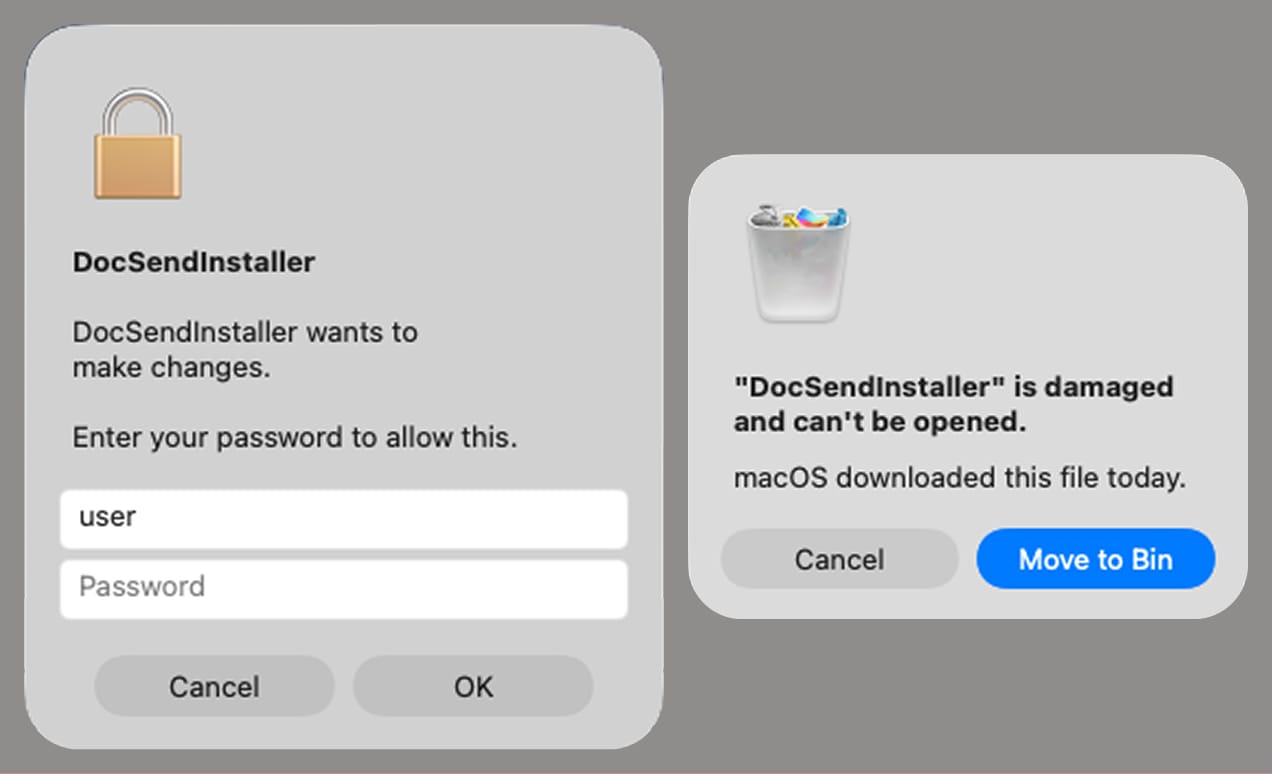
It is also recommended to avoid downloading DMG files from suspicious websites and treat administrator password prompts with caution.



