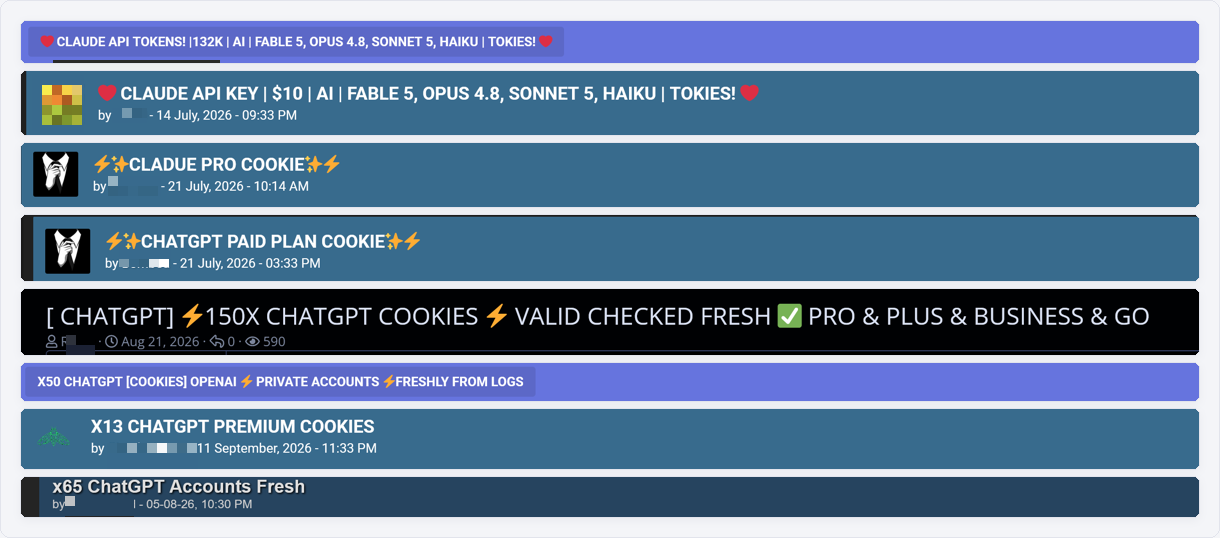
The summer of 2026 taught the security industry a new term: the stolen AI login. As BleepingComputer reported, in late August, Anthropic responded to Infostealer’s takeover of Claude sessions by logging out users, deleting saved payment methods, and refunding charges identified as unauthorized.
This is the supply side. SOCRadar’s AI Identity Exposure Report it’s about the demand side: the companies whose employees are the references that are being sold.
Starting from more than a million Infostealer records linked to AI services across more than 80,000 enterprise domains, the research narrowed the set to 482 large incumbents to answer a single question: If an AI login ends up in a Stealer log, who owns it and what does the buyer inherit?
Of the 482, 68% are billion-dollar organizations in 36 countries and eight sectors focused in North America, dozens of which are in the Forbes ranking.
Among them are 5,434 stealer log records linked to 1,500 different corporate email addresses, and 295 of the 482 appeared in the last 90 days.
ChatGPT dominates the dataset; The Hugging Face and Replit Show developer tools are also featured
Split the data set by platform and one name swallows the chart. A captured ChatGPT or OpenAI session appears for 358 of the 482 companies, and these companies contain approximately 90% of all records in the study. Zapier, Notion, Hugging Face, Replit, Lovable and ElevenLabs are far behind.
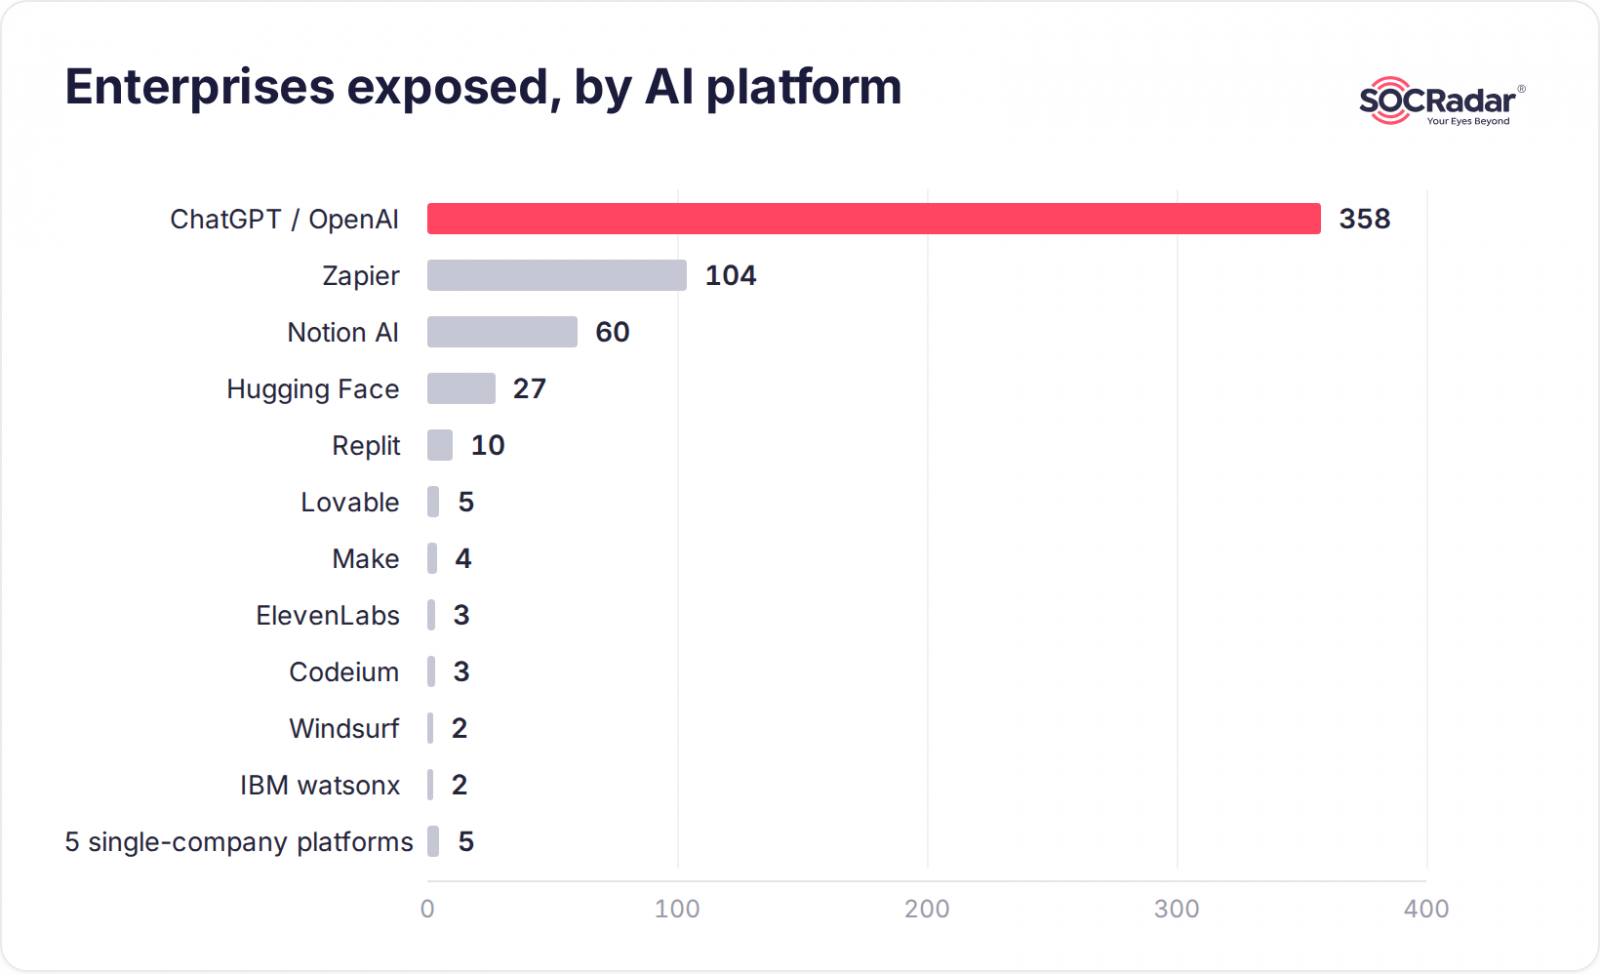
This distortion is important, but the more interesting part is who is missing. There is no Claude in the top ranks. No twins.
|
Researcher’s comment
“We interpret ChatGPT’s near-total dominance as a shadow AI signal, rather than a judgment about a provider’s security. Its first-mover advantage means far more employees have quietly signed in with a work email address on a personal device, and that’s the population infostealers’ problem. As adoption of other assistants catches up, we expect this trend to level off.”
|
This is a timely reservation. Anthropic’s own incident at the end of August showed that Claude sessions are targeted once they are in sufficient quantity; The platform simply has a smaller corporate footprint today.
The lesson for a CISO is not to “choose a safer assistant.” It’s because disclosure follows users and users are everywhere your policy isn’t.
Enter a work domain to see which AI platforms show stolen employee logins, how many records, and how recent.
No registration required, updated daily on 44 AI platforms.
Why a stolen AI login is worse than a stolen password
An app is activated with a conventional proof of authorization. An AI account is four things at once: a searchable archive, an execution engine, a billable resource, and an identity. A stolen session passes all four without a password prompt.
The course of the conversation is the break
Employees insert source code, customer records, contracts, and unpublished plans into prompts. The account becomes the repository of the corporate storage, and whoever replays the session inherits this archive before touching any internal system.
Session cookies bypass MFA
A stolen cookie is a live session. As Okta’s Jeremy Kirk put it, session tokens and API keys are wanted precisely because they can be replayed to bypass credential-based authentication. Rotating the password keeps the intruder logged in.
Agents act with the authority of the employee
Automation platforms have ongoing OAuth grants for CRM, email, and storage. A stolen Zapier session allows an attacker to create a workflow that filters data from a provider’s trusted IP range on a schedule.
API keys are Money, Capacity and Coverage – LLMjacking
Keys copied to a notes app or workspace settings page are stolen along with everything else and then billed to the victim or resold. Underground traders offer discounted access to Claude, Gemini and Cursor accounts as well as money-back guarantees.
Technology is leading the way, but attention is everywhere
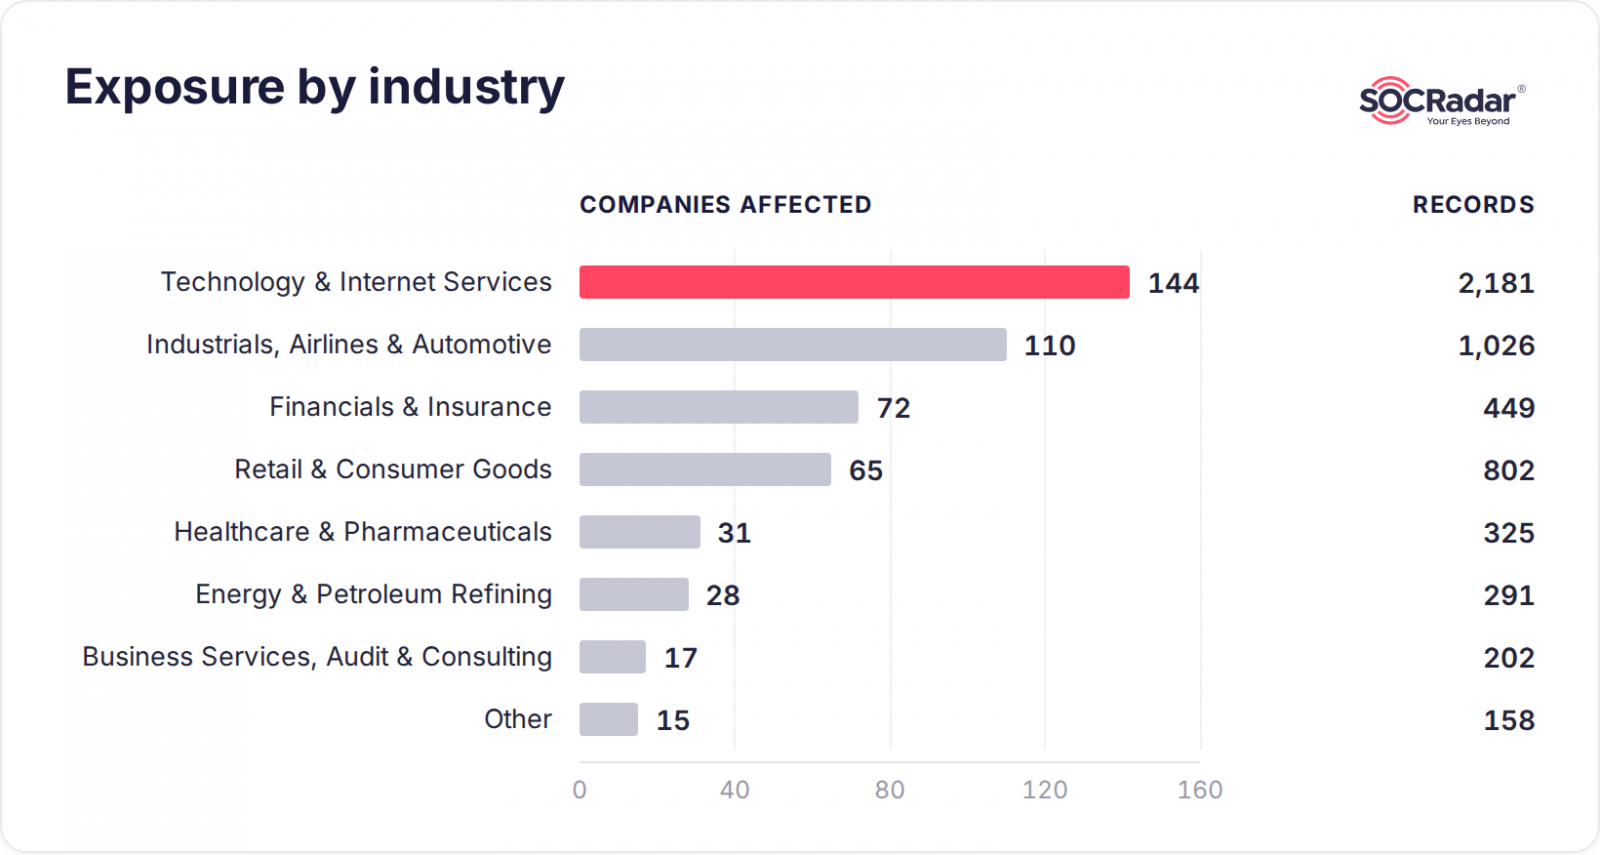
Technology and Internet services companies represent the largest single group, with 144 companies and 40% of all data sets, and these companies have data for many downstream customers.
Industrial, financial services, retail, healthcare and energy all appear to be well represented.
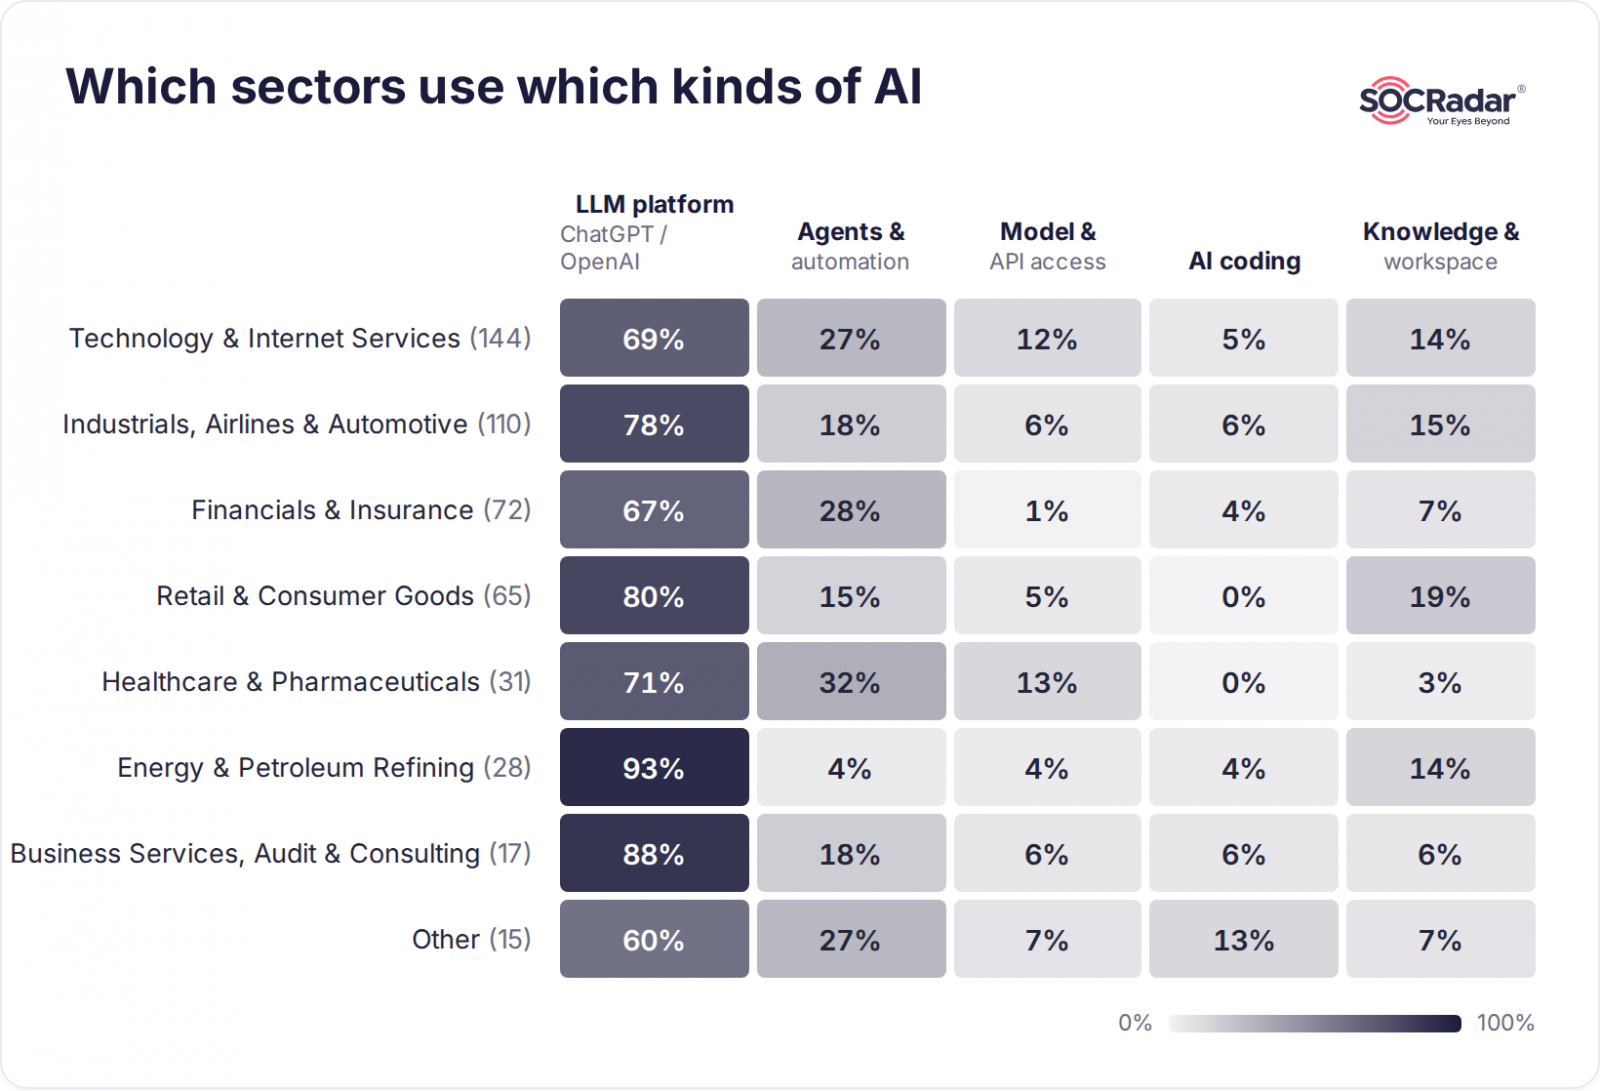
Divide the same sectors by what type of AI is exposed and the risk profile shifts. Exposure to LLM platforms is almost universal, with 93% of affected companies being highest in the energy sector.
Agent and automation exposure that transfers an employee’s authority to other systems is focused on healthcare, financial services and technology.
None of this requires an autonomous swarm of agents. An employee, an unmanaged laptop, a saved ChatGPT password and a commodity infostealer for sale in Telegram channels since 2022 are enough.
What to do about it?
The controls are not exotic. What’s new is that AI platforms are now on the same level as your identity provider and code repositories.
- Put any AI platform behind SSO with short-lived sessions: Use OAuth 2.0/OIDC with refresh token rotation to allow a stolen cookie to expire before it can be sold. SSO removes the saved password, not the live session cookie, and takes no action on accounts opened before the policy passes.
- Restrict, limit and rotate API keys: Notification when used by unknown ASNs or at unusual times – the fingerprint of LLMjacking.
- Monitor session token reuse: A session that changes the country or fingerprint of the device mid-life is a repeated session. Treat any employee that appears in a stealer log as an endpoint incident, not a password reset.
- First find the shadow accounts: You can’t shoot something that you don’t know exists. First, find out which of your domains are already showing up in stealer logs. You can use SOCRadar’s free AI Identity Exposure tool.
Conclusion
Anthropics Answer For his own incident, the template is worth copying: it invalidated sessions, removed the payment methods abused by the attackers, and notified the people whose computers were infected before the scam reached them.
View the full report from SOCRadar.
Sponsored and written by SOCRadar.



