The ShinyHunters extortion gang uses a URL encryption trick to bypass web application firewall rules that mitigate the Oracle PeopleSoft CVE-2026-35273 vulnerability, allowing threat actors to re-exploit the vulnerability on vulnerable servers.
Mandiant and Google’s Threat Intelligence Group (GTIG) say this new technique allowed the threat actor to once again target PeopleSoft servers that had not applied security updates and instead blocked access to the vulnerable PSEMHUB endpoint using a WAF.
On June 10, BleepingComputer first reported that the ShinyHunters extortion gang targeted Oracle PeopleSoft servers using a zero-day vulnerability and was able to steal data from 100 organizations.
The next day, Oracle corrected the PeopleSoft zero day as CVE-2026-35273, stating that it allowed unauthenticated remote code execution.
Google also reported on the same day that ShinyHunters, which they track as UNC6240, exploited the CVE-2026-35273 vulnerability to attack the education sector, confirming BleepingComputer’s reporting.
At the time, Mandiant advised organizations that were unable to immediately install the security updates or disable the Environment Management Hub to block external access to the vulnerable endpoint /PSEMHUB/*.
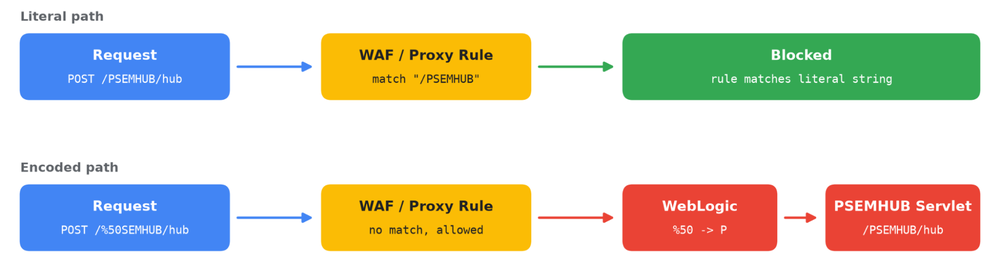
However, in one new reportAccording to Google, ShinyHunters has now modified its exploit to bypass WAF rules that look for this literal path instead of encoded versions of it.
For example, instead of sending requests to:
/PSEMHUB/
The attackers demand:
/%50SEMHUB/
The sequence “%50” is the percent encoded version of the letter “P”.
According to Mandiant, many WAFs and reverse proxies compare the literal request path before decoding it, causing rules intended to block /PSEMHUB/ to miss the encoded version.
Oracle WebLogic, on the other hand, decodes the encoded “P” and forwards the request to the vulnerable endpoint, bypassing the WAF rule.
“This allows the threat actor to reach the endpoint on systems whose operators may have believed that their WAF rules would have mitigated the compromise,” Mandiant explains.
Source: Mandiant
Google warns that ShinyHunters may not always use the “%50” bypass variant and may switch to other percent-encoded, mixed case, or other variants of “/PSEMHUB/” to bypass WAFs.
Instead of relying on a web application firewall, Mandiant strongly recommends that organizations install the latest security update to protect against CVE-2026-35273.
Organizations are also recommended to search WebLogic access logs for requests to “/PSEMHUB/” and encoded variants such as “/%50SEMHUB/” to identify signs of exploitation.
WAF bypass leads to new data theft attacks
According to Google, the new wave of attacks has deployed web shells on dozens of systems worldwide in higher education, technology, IT services, healthcare, agriculture, transportation and government organizations.
“Mandiant recommends that organizations using Oracle PeopleSoft take the following immediate actions. Additional remediation and hardening guidance can be found later in this post,” warns Mandiant.
Before attackers attempt an attack, they typically send between five and 15 POST requests to /%50SEMHUB/hub containing serialized Java objects.
On vulnerable systems, these requests return information about the host operating system without writing files or interrupting service, allowing ShinyHunters to determine whether a server can be silently exploited.
Once they determine that a system is vulnerable, threat actors re-exploit the vulnerability to execute commands directly in memory or deploy JSP web shells.
According to Google, the attackers use an “x.jsp” web shell for command execution as well as “u.jsp” and “u2.jsp” shells for uploading larger files.
On compromised Windows servers, ShinyHunters used these shells to deploy an executable file called “Ple64.exe” that masquerades as a signed Light Alloy Media Player installer but installs a backdoor tracked by Google as SIDEEYE.
The SIDEEYE malware is used for credential theft, process and file management, creation of interactive reverse shells, and reverse proxy functionality.
The threat actors also used open source Neo-reGeorg tunneling toolkit via the “tunnel.jsp” and “tunnel.jspx” files.
This toolkit allows SOCKS5 proxy traffic to be tunneled over regular HTTP and HTTPS connections, allowing the compromised PeopleSoft server to be used to propagate laterally into the internal network.
Mandiant also observed that ShinyHunters used legitimate remote management software MeshAgent to maintain access to compromised Linux systems.
ShinyHunters previously claimed a new zero-day from PeopleSoft
These new attacks came after ShinyHunters claimed they had penetrated FBI systems by exploiting a new zero-day vulnerability from Oracle PeopleSoft.
ShinyHunters told BleepingComputer on September 22 that the alleged vulnerability allowed remote code execution and was used to access the FBI Jobs platform, then spread laterally into the FBI’s AWS GovCloud infrastructure.
The group said it stole between 2 and 3 TB of data from current and former FBI employees, applicants and other internal systems.
At this time, BleepingComputer could not independently verify the alleged zero-day, the alleged lateral movement, or the amount of data allegedly stolen.
The FBI confirmed that it was investigating allegations of unauthorized activity involving FBIjobs.gov, but did not confirm that its systems had been breached or that data had been stolen.
ShinyHunters confirmed to BleepingComputer that they used this WAF bypass against FBI Jobs, but further claim that they also exploited “NEW unknown vulnerability in the same PSEMHUB component.”



