After suspected North Korean hackers exploited crypto exchange BitJet for $387.5 million last week, investigators were able to quickly flag and identify recipient addresses.
Bitgate CEO Gracie Chen then controversially claimed that the decentralized cross-chain swap platform THORchain “denies service to these addresses.”
THORChain replied:
“Thorchain is decentralized and permissionless like Bitcoin, Ethereum, and BNB chains. What responsibility should Bitcoin, Ethereum, and BNB chains bear when handling known stolen funds?”
The move was controversial, especially since the protocol was immediately shut down in May when $10.7 million of its own funds were embezzled. Complicating matters, THORchain has retired its admin key and has no easy way to censor addresses, even if it wanted to.
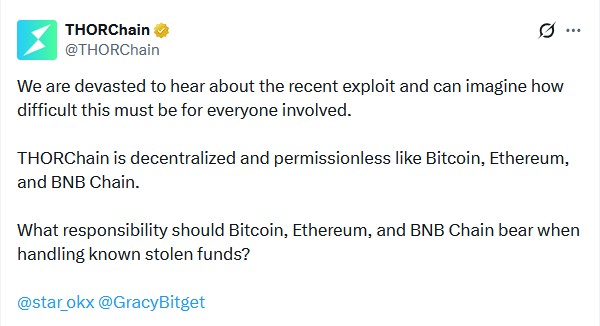
Source: THORchain
This exact debate has come up before, as ThorChain was used to swap around $1.2 billion in funds for a $1.46 billion hack of ByBit. It just so happened that THORChain’s admin key retired just 11 days ago.
NEAR Intents has taken the opposite approach to THORchain. Its automated SHIELD program blocked addresses linked to the hack from exchanging $50 million on the platform, and even rejected the 5% bounty BitJet was offering to do so.
Now NEAR Intents are under fire from decentralized Maxis for not being permissionless enough.
To discuss the legal issues involved in the case, the magazine spoke with Yuri Brisov from D&A Partners. This is an edited version of the conversation.
Magazine: Bitget asked THORchain to block funds linked to the hack and responded that it was decentralized and permissionless. Is it a legal defense? Do they have an obligation to block those addresses?
delete: It depends on the level of decentralization. So when they do this – when they block some addresses – they show that their nodes are not really decentralized. It is good for the community, when they can use this power to prevent some malicious activities. However, at the same time, they open themselves up to other legal claims. Their only defense is “we are decentralized.”
In the Uniswap case, they said ‘we’re really decentralized and we don’t have to do anything.’ (Investors sued UNISAP after 38 ragpool and scam token purchases, but a judge Case dismissed March -Ed.)
And this is the strongest defense for any DeFi protocol. If they show that they can block, control or interfere in some way – even a good-faith attempt to prevent fraud – they still open themselves up to such claims. That if you have control, maybe your control is not limited to obvious fraud. You should understand the issues of due diligence (regulation). You should implement KYC and AML safeguards.
Related: Uniswap Beats Class Action Alleging It Aids Crypto ‘Rage Pull’
Magazine: NEAR Intents blocked those addresses, and Bitget thanked them for doing so. Does this mean that NEAR showed Intents are not decentralized and therefore must intervene in many other situations?
If you show that you have control over the assets, you potentially open yourself up to all possible claims related to pump-and-dump schemes, volatility, or any other potential claim by any investor who has been harmed and harmed in some way. And they can now say that you have control. Why would you use it in one case and not in another? Why don’t you check all your token issuers on your platform? Why they don’t provide KYC forms like any centralized exchange?
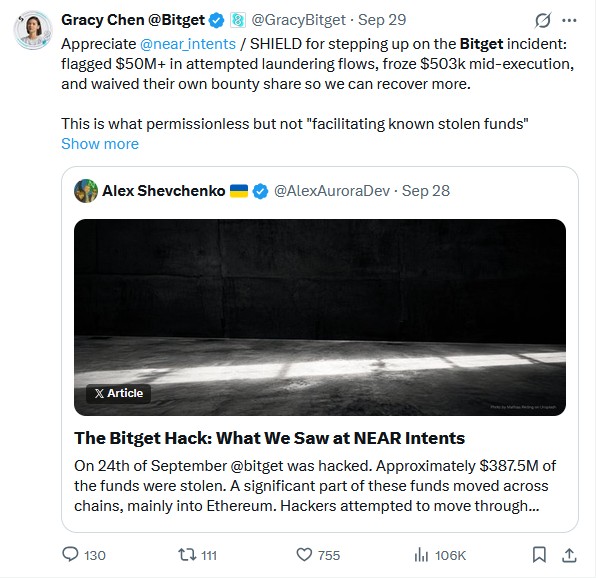
Source: Gracie Chen
Magazine: THORchain argues that the protocol suspension in May was initially triggered by an automated system and that they do not have the ability to block specific addresses. If true, is this a defense?
delete: It could be. We don’t know yet, because it hasn’t been challenged yet. But any amount of regulation makes any DeFi project vulnerable to any claimant.
Magazine: On the other hand, Protocol Software can upgrade if it wants to block specific addresses. Can a project get into legal trouble due to recklessness or negligence if they don’t impose something like this?
It depends on how it is done technically. Say there’s an oracle that can detect any North Korean IP and block it automatically, and there’s no person who sits down and presses a button – “There’s a North Korean hacker, let’s block him.” Then it’s okay.
If there’s a team that monitors the situation and says, “OK, we see this is illegal activity, we block these addresses, we push the button manually.” From a legal point of view, although this is a good thing and it benefits the community, it does not fully decentralize the project from a legal point of view and it deprives you of the protection that regulations like MiCA (EU’s Markets in Crypto Asset Laws) or the general understanding of the SEC and CFTC provide that if you can be part of a completely decent behavior, you cannot be completely qualified. ecosystem
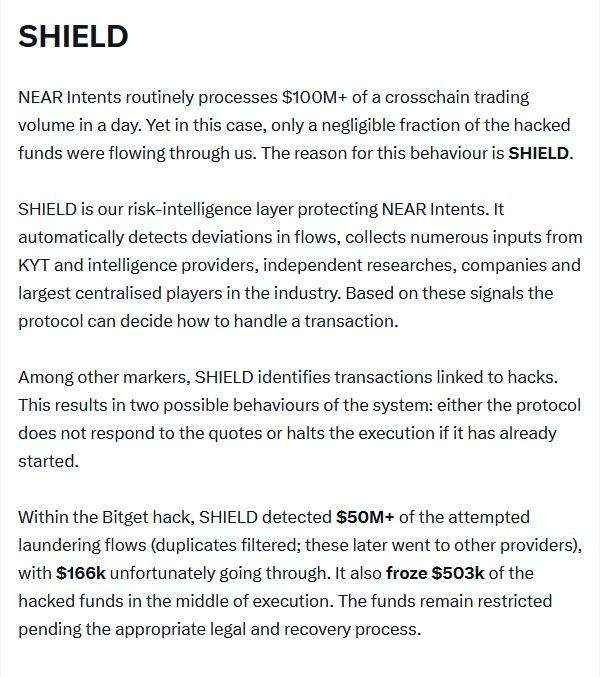
Source: Alex Shevchenko
Magazine: NEAR’s technology is called SHIELD And it’s an automated process that detects addresses associated with known hacks on public blockchains and then automatically blocks those intents from accessing them. Does this mean it is more likely to be seen as decentralized?
delete: of course They show that they are good-faith actors by trying to (add) protective measures to their protocols. There is no compliance team, who sit there and manually control operations. This is a smart solution, and one we recommend to all DeFi companies
Magazine: In February 2025, THORchain retired the admin key which allowed them to make unilateral changes. Since there isn’t an admin key and they’ve got a hundred validations, does that make them decentralized enough?
delete: More likely not, but we can’t say for sure. I would say yes.
Magazine: THORchain is not a mixer. You can take the stolen Bitget funds and swap them to THORchain, but when it comes to the other end, it will still be transparently connected to the Bitget hackers. How does that fit the definition of money laundering? Or getting stolen goods?
delete: I don’t see how they can be liable for money laundering because even Tornado Cash, which was created to launder a certain amount of money (U.S. sanctions have been avoided because immutable smart contracts are property-enforceable in money laundering cases)
American law does not consider anything to be property or property. And money laundering is the illegal transfer of property through legitimate means. You get income from illegal activity, and it’s property, and then you move it through some channel and try to make it legal. But smart contracts are not property at all. You do not control them. You do not own them. That’s how Tornado Cash won their case in court against the OFAC ban. They just proved that they have no control over their smart contracts.
Magazine: The Bybit hack happened 18 months ago. Does that mean that no legal action is being taken against THORChain, or do these cases take a long time?
delete: It could happen in the future, of course. After the Bybit case, they seriously opened themselves up to potential claims.
magazine: The Big Question: Does Satoshi Really Own 1.1 Million Bitcoins?
Cointelegraph publishes long-form journalism, analysis and narrative reports with subject-matter expertise developed by Cointelegraph’s in-house editorial team. All articles are edited and reviewed by Cointelegraph editors according to our editorial standards. Some articles contain affiliate links, from which Cointelegraph may earn commissions. These relationships do not influence which products we review or our editorial decisions The content published here does not constitute financial, legal or investment advice. Readers should conduct their own research and consult with appropriate professionals. Cointelegraph maintains complete editorial independence.