A malware campaign dubbed “Midnight Mimosa” has been discovered on low-cost Android smartphones that ship with malware embedded in their firmware, allowing attackers to silently install apps, conduct ad fraud, and turn devices into private proxies.
The malware is believed to have been introduced somewhere in the device’s supply chain. However, it remains unclear who is responsible for changing the firmware and at what stage the manipulation took place.
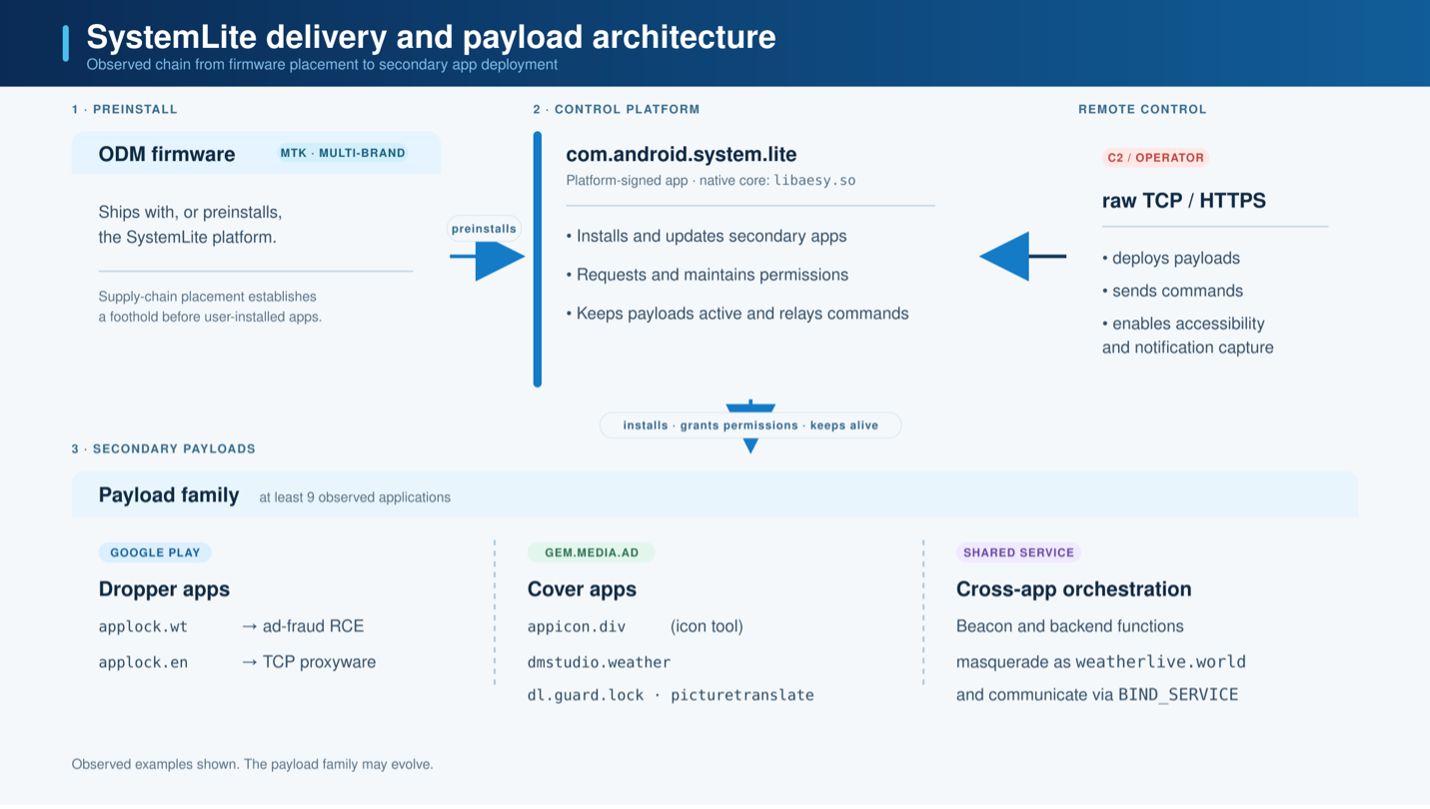
The malware is embedded directly into the firmware of low-cost Android devices using MediaTek chipsets, giving it system-level permissions that allow it to install and remove applications, grant sensitive permissions, and remotely execute downloaded code without user interaction.
Accordingly Bitdefender researchersOver the course of approximately two years, the campaign affected thousands of devices in more than 150 countries, with the largest number of victims occurring in Mexico, France, Italy, the United States, Germany, Brazil and Spain.
Researchers found pre-installed malware on devices with model names associated with legitimate manufacturers, including Doogee S200 X and Cubot KINGKONG X, as well as on phones masquerading as Samsung and Apple products.
In one Post in the XDA forumOwners of Cubot and Doogee smartphones reported that they found suspicious applications that repeatedly reinstalled themselves after being removed.
A Doogee Fire 3 Max owner too reported that an official firmware update infected the device with the malware, which disappeared after restoring an older firmware version, but returned after reinstalling the update.
Some users said manufacturers released firmware updates that fixed the infections. However, the manufacturers have not publicly explained how the malware was introduced into the affected firmware.
Bitdefender also mentioned the XDA forum post in its report and said one of the malware packages reported by forum users was: com.android.non.szczis part of the same malware family.
Pre-installed Android malware
Unlike typical Android malware that requires users to install a malicious application, Midnight Mimosa is already installed in the device’s system partition when customers receive their phone.
The malicious programs imitate legitimate Android system packages and use names like “ com.android.system.lite, com.android.sys.protAnd com.android.sys.gmsprot.
Since these applications are signed and run with elevated system privileges, they cannot be removed through the normal Android application uninstallation process.
Bitdefender discovered the campaign after its app Anomaly Detection technology detected a suspicious system application called “ com.android.system.lite that was the silent installation and removal of other applications.
Further investigation revealed that the application was part of a larger malware framework that downloads additional modules from command and control (C2) servers to carry out various malicious activities.
The researchers identified about 32 applications distributed across the framework, including apps disguised as weather utilities, file managers, app closers, OCR tools and audio editors.
“The system app itself does not register the fraudulent impressions and clicks,” explains Bitdefender.
“The revenue engine is powered by the drop cover apps, including real-looking weather, app locking, note-taking and OCR apps that load real ads via a legitimate ad SDK. The goal is simple: load an invisible window on top of the apps that registers the ads being displayed.”
These applications are used to generate fraudulent advertising impressions and clicks. Some display advertisements in hidden windows or automatically interact with advertisements without the device owner’s intervention.
The malware also uses techniques aimed at bypassing Android’s security measures.
Before malicious applications are silently installed, the Google Play Store app is temporarily disabled. com.android.vendingwhich, according to Bitdefender, is intended to prevent Google Play Protect from recognizing the installation.
After the installation is complete, the malware activates the Play Store again so as not to arouse suspicion.
Some malware variants also manipulate Android’s recorded installation information to make it appear that malicious applications were installed via Google Play, even though they were served directly by the malware.
The malware also includes features that turn infected Android phones into private proxies that can route network traffic.
Bitdefender has identified a malicious application disguised as App Locker. com.mobile.applock.enwhich contains a TCP proxy component that registers infected devices with a remote command server.
Once registered, the malware can be sent instructions to connect to specific hosts and route traffic through the infected device.
This could allow attackers to route malicious traffic over phone owners’ Internet connections, obscuring the true origin of the attacks or allowing access to devices reachable from the infected device.
Bitdefender confirmed that the proxy command and control infrastructure was operational and accepting device registrations.
However, during their testing, the researchers reported that their newly registered device did not receive any relay targets, so they could not confirm whether the attacker was actively forwarding the traffic.
Source: Bitdefender
Researchers also discovered 13 Android applications distributed through the Google Play Store that contained the same ad fraud code and communicated with the well-known Midnight Mimosa infrastructure.
Unlike the pre-installed system components, these applications do not have elevated privileges required to silently install other software.
However, they can still display advertising outside of their interface even when users are not using the phone.
The applications were distributed using 13 different signing certificates and at least two developer accounts identified as fivedev And CPS Developer.
Researchers also found firmware signed with certificates from Chinese device maker Shenzhen Zediel, but said it was unclear whether the company was involved in the malware campaign.
For affected consumers, removing the malware is difficult because the malware is installed as a highly privileged system application.
According to Bitdefender, removing the infection requires a firmware-level cleanup or disabling the malicious component using the Android Debug Bridge (ADB), which may be complicated for many users.



