
A critical heap buffer overflow vulnerability (CVE-2026-39919) in the Ghostscript interpreter and rendering engine could allow remote code execution via specially crafted PDF files.
The flaw was discovered on August 23 by researchers at Defiant platform Wordfence using their AI-powered system Argus.
Ghostscript is a PostScript and PDF interpreter that can render PDFs as images, create thumbnails for previews, and optimize PDF files by compressing embedded images and removing unnecessary font data.
When generating a PDF thumbnail, WordPress can use the Imagick PHP extension to call ImageMagick, which launches Ghostscript.
A specially crafted PDF file containing a JPEG 2000 image may result in incorrect processing of low bit depth samples and mismatched component resolutions.
Using Argus, researchers developed two exploits for CVE-2026-39919 that force Ghostscript to write 1,024 bytes to a 256-byte buffer, corrupting nearby memory and leading to unauthenticated remote code execution in a WordPress deployment.
Wordfence focused on WordPress systems, but notes that the flaw affects any online system running Ghostscript 9.21 through 10.07.1 and is exploitable if the payload is tailored to the environment.
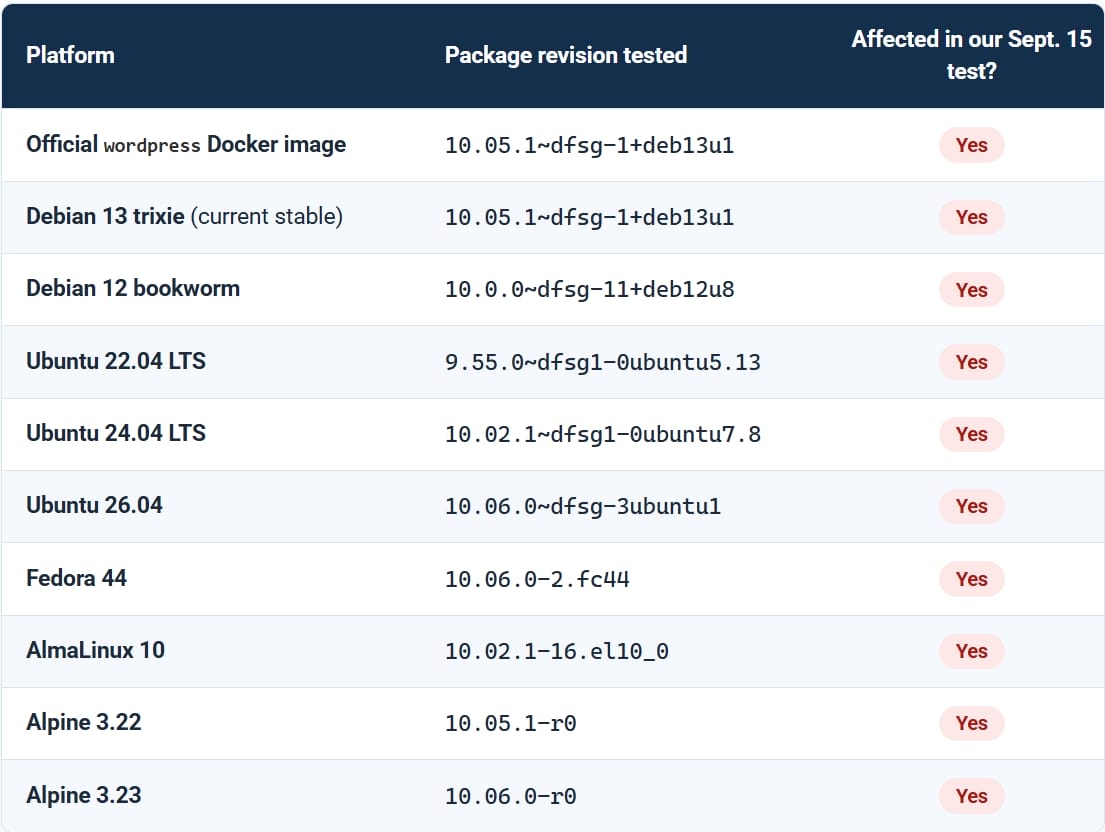
The researchers tested ten Linux environments, including Debian, Ubuntu, Fedora, Alpine and AlmaLinux, as well as an official WordPress Docker image snapshot, and found that all contained the vulnerable code.
Source: Wordfence
Researchers tested two proof-of-concept (PoC) exploits and found that their ability to trigger the vulnerability depends on the target environment.
In a lab test environment, they ran the exploits 10,240 times against Linux packages but were unable to achieve remote code execution. However, they successfully ran the code remotely on a purpose-built test server.
The researchers found that changing the PDF file’s fonts, language settings, font configuration, and a core system library allowed the exploit to succeed, although not reliably.
Especially in WordPress environments, four prerequisites are required for successful exploitation:
- An attacker can upload a PDF anonymously or through an account with low privileges.
- The site processes this PDF file to create a preview or thumbnail.
- The processing chain reaches Ghostscript, with the necessary software and policy settings enabling PDF playback.
- Ghostscript contains the unpatched vulnerable decoding code.
Wordfence discovered that the default WordPress does not allow anonymous uploads to the media library.
In general, any application that renders attacker-supplied PDFs via affected Ghostscript code can expose the flaw, and the authentication requirements for exploitation depend on the application.
Artifex, the maintainer of Ghostscript, released a fix in version 10.08.0 of the interpreter on September 8th.
Fixes have also been backported to older versions, so users should check the revision details for patch status.
WordPress administrators must ensure through their hosting provider that Ghostscript has been updated to version 10.08.0 or later.
If you are using Docker, it is recommended to rebuild and redeploy with an updated, patched base image.
If it is not possible to upgrade to a fixed version of Ghostscript, it is recommended to block PDF uploads to the server or disable PDF playback in ImageMagick.
Wordfence stated that there has been no exploitation of CVE-2026-39919 in the wild.


