The Candiru spyware was delivered to Al Jazeera Media Network’s devices via targeted online advertisements in a zero-click attack that only required the malicious ads to be displayed on the victim’s device.
Citizen Labs researchers who investigated the attacks called the technique AdFection and noted that their report was the first public technical confirmation of mercenary spyware spread through targeted advertising.
A similar method was documented by Amnesty International in late 2025, involving ads that infected targets with the Predator spyware without them clicking on anything.
This infection mechanism was dubbed Aladdin and emerged due to a collection of marketing files and documents leaked by surveillance company Intellexa, which were examined by researchers and backed up with technical details from forensic investigations.
Unlike Alladin, AdFection has been implicated in real attacks and has been linked to Israeli firm Discovere-Tech, described by Citizen Lab as a “bridge between mercenary spyware companies and the advertising ecosystem.”
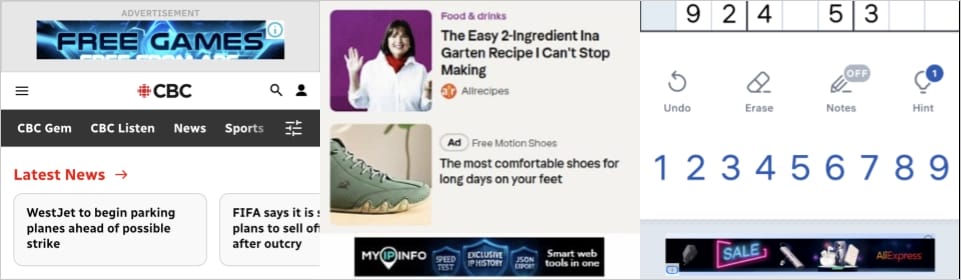
Source: Citizen Lab
Zero-click Candiru spyware infection
According to Citizen Lab, Discover-Tech allowed its customers to use its Controlium platform to attack specific devices with malicious code or to profile, de-anonize, and fingerprint user devices.
“Discover-Tech appears to be working with several mercenary spyware, hacking and advertising providers, connecting the spyware industry with the online advertising ecosystem.” Citizen Lab says.
The company purchased ad placements across popular ad networks and exchanges and embedded JavaScript into ads that contacted their “NOAS server” when played.
Using several parameters (e.g. IP address, ad identifiers), the NOAS server “or getAd server” determined whether a target was authorized to receive JavaScript code.
Selected targets received additional code, while other devices rendering the display received none, helping the attacks remain stealthy.
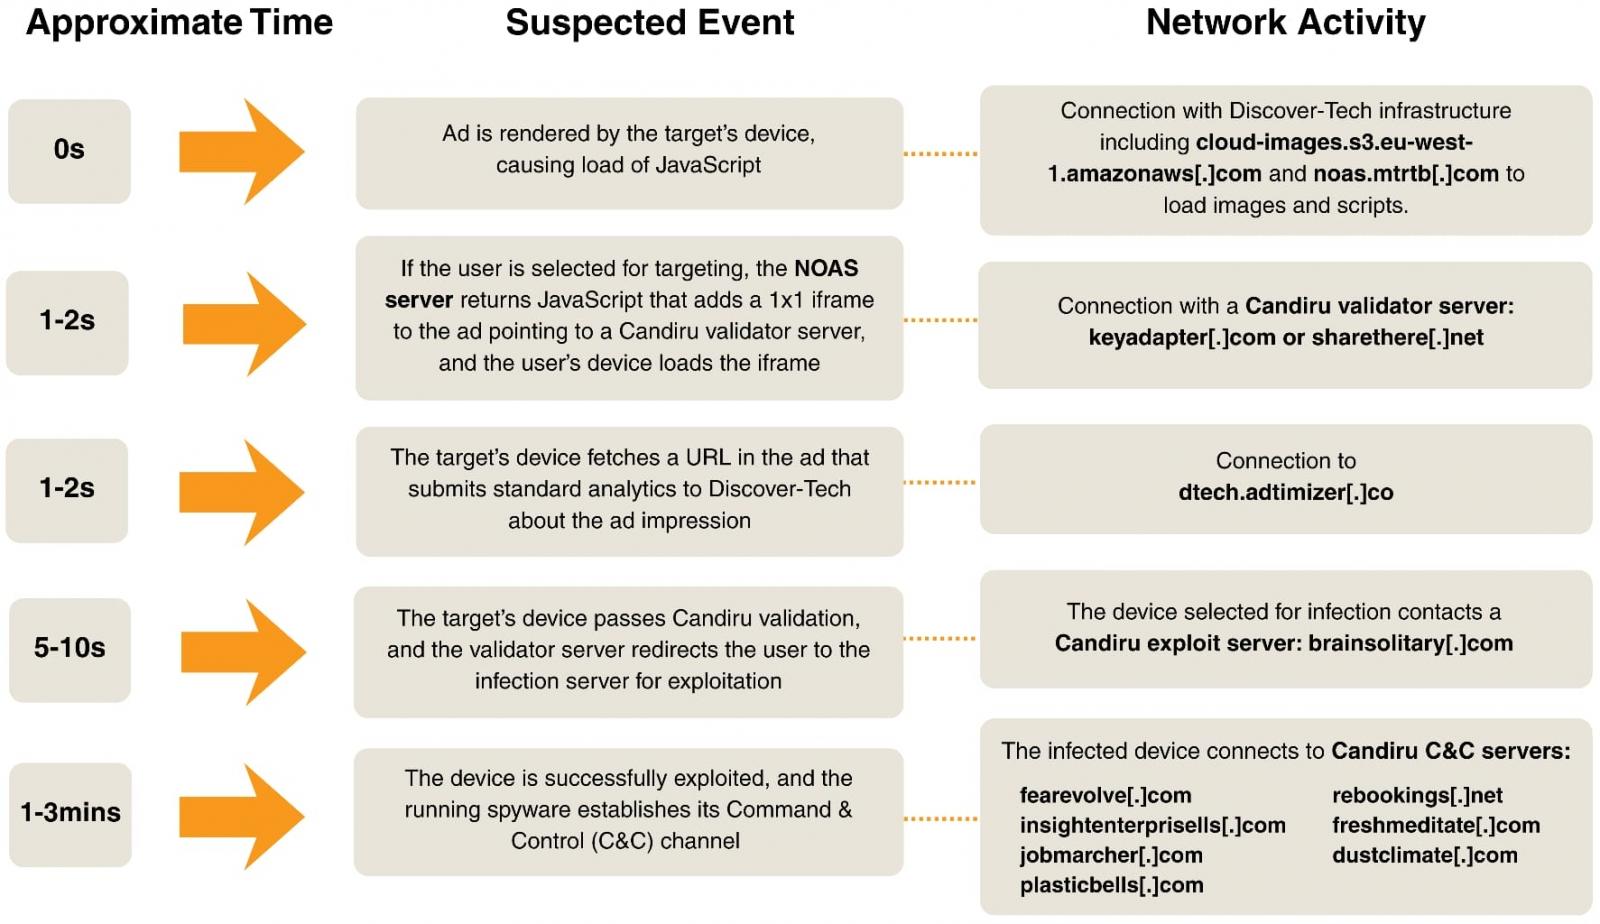
Source: Citizen Lab
Al Jazeera provided Citizen Lab with evidence of attacks that targeted at least 45 devices between 2024 and 2025. The network logs examined by the researchers showed a sequence from Discover Tech infrastructure to Candiru validation servers to spyware command and control servers.
Researchers also recovered a DLL file from a compromised Windows system and attributed it to Candiru with high confidence based on infrastructure and code overlaps with previously captured examples.
Candiru is an Israeli spyware provider that officially only sells surveillance tools to governments. The company has also developed a malware for Windows called DevilsTongue that can steal files, credentials and messages.
Previous reports said its tools were used against journalists, activists, politicians and other targets via Windows and Chrome zero-day exploits.
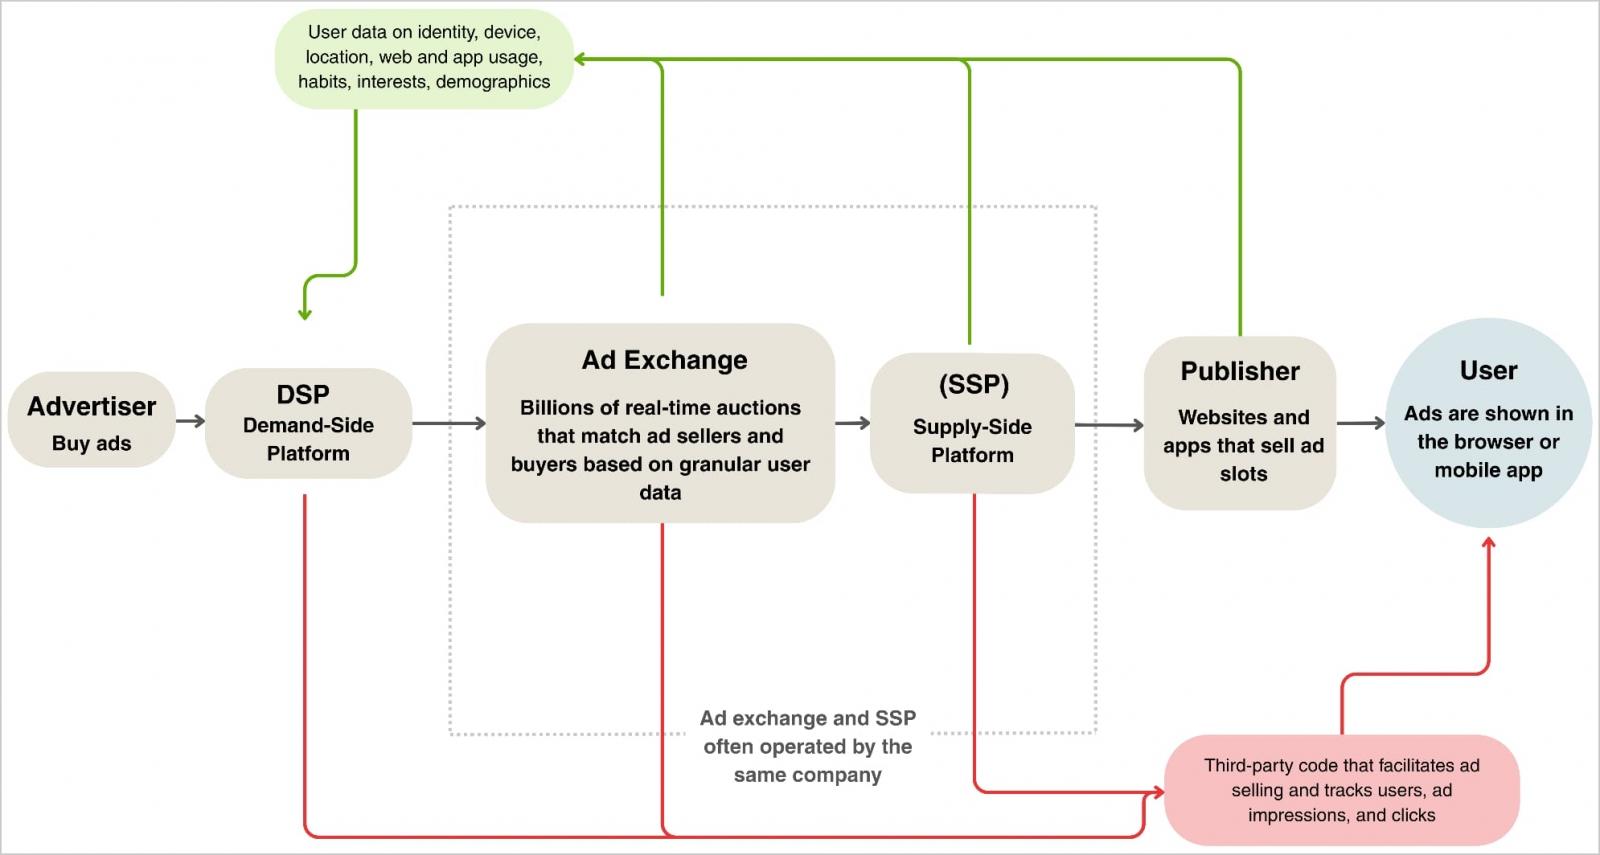
Source: Citizen Lab
While Al Jazeera is a confirmed target of these attacks, Citizen Lab reports that the advertising company placed 3.77 billion bids and won 442 million auctions between March and June 2026.
75,373 Android/iOS apps and 120,768 websites were shown ads that were found to contain attacker script tags. However, these numbers do not represent infection numbers.
“We estimate that between hundreds of thousands and millions of users were directed to these domains through Discover Tech ads,” explains Citizen Lab.
After receiving Citizen Lab’s reports, major advertising companies such as Google, IAB Europe, Beeswax, Eskimi and Vungle took action to remove offending accounts and block access to domains.



